Technologies
Over Half of Us Have Faced Possible Malware, Yet Some Are Ignoring Cybercriminals
Protecting your devices and data takes a lot more than antivirus software.
When you see a malicious email or link, you may already have your next steps in mind, like deleting it right away, reporting it as spam and even blocking the sender. However, CNET’s latest survey found that some US adults don’t take any action at all.
It’s easy to comfortably assume that antivirus software and other cybersecurity tools will protect you from malware, but scammers are still finding workarounds to steal our data. In fact, even though many devices have built-in antivirus protection, over half (54%) of US adults with personal laptops have encountered potential malware within the past year.
Your first step when you notice a possible malware attempt is the most important. Clicking a link out of curiosity can lead to a virus, identity theft or even fraud. However, ignoring it isn’t the best course of action either.
We can help you navigate these instances. Here are CNET’s latest survey findings and information for how far CNET’s experts say antivirus software can really protect you from phishing headaches and hassles.
Laptop owners have encountered phishing emails the most
My mom just got a new laptop and told me she doesn’t need antivirus protection. She’s not entirely wrong. CNET’s antivirus experts, Moe Long and Attila Tomaschek, say you don’t necessarily need another antivirus program if your device already has built-in antivirus protection — as most computers today do.
Windows 11 includes Microsoft Defender antivirus protection. Mac users have XProtect to check for malware, while the Malware Removal tool catches anything XProtect may have missed. And the Gatekeeper feature stops you from opening apps and software that aren’t trusted. But viruses, phishing and malware attempts are still lurking, as CNET’s study shows.
CNET found that over the past year, US adults who own a laptop have encountered or interacted with phishing emails most often (37%), followed by urgent pop-ups (24%), unusual payment requests (17%), and branded spoofing (17%).
Cybercriminals are using artificial intelligence to make scams more believable — even through impersonation. And they’re coming up with new tactics much faster than in the 1990s, when we all took our desktops to the Geek Squad for help after a scammer’s successful malware attack.
But here’s the most important distinction to know: Antivirus software may not be able to help identify phishing and malware attempts that are constantly evolving. It can help prevent malicious software from attacking your device and personal data, so long as that malware is in its database of known threats. But you’ll need to use your best judgment to avoid clicking those suspicious links first.
88% of US adults took action after seeing potential malware
CNET found that 88% of US adults who own laptops took action after coming across potential malware over the past year. That’s encouraging news for Long and Tomaschek.
“You don’t really want to mess around with malware, especially the way a lot of modern malware is designed to get your data instead of crashing your computer or something like that,” Long says.
Here’s a closer look at how laptop owners take action.
Over half (60%) of US adults either manually deleted the file or closed a website or pop-up, and 35% immediately ran an antivirus or anti-malware scan. However, Long says some of these actions are effective and helpful, while others aren’t.
If there’s a malicious pop-up, and you close it without clicking a link, you may not have to worry about malware or a virus, Long says. If you download a malicious file, you might be able to delete it before it does any harm. But if you download an executable file, like a software application that infects your device when it’s run, you could actually be installing malware on your computer along with what you think is just an application.
Some actions are definitely worth taking, like immediately running an antivirus or anti-malware scan after encountering malware (35%), says Long.
But other actions aren’t, like installing a VPN, which 8% of US laptop owners do, according to CNET.
Long says that a VPN is a privacy tool, and it has very few security benefits. If you’re using a VPN on a public Wi-Fi network that’s under attack, a VPN can mitigate the risk of the attack reaching your device. But for the most part, VPNs are just another part of your cybersecurity toolkit, but for privacy, not online security, says Tomaschek.
The best course of action if you believe your computer is infected with malware is to perform a factory reset to wipe your hard drive clean, leaving nothing behind from the current state. You’ll also need to make sure you don’t restore from a backup where you had that malware infecting your machine, Long says. Keep in mind that it won’t erase any information that attackers may have retrieved.
There are other measures you can take to try resolving a potential malware infection without a factory reset. Long recommends disconnecting your device from the internet to prevent it from infecting other devices on your network. Then, try using advanced malware scanners, like Microsoft Defender’s offline scanner, to try to find and resolve any threats. But be careful — infected files could harm other devices if you transfer them.
There’s not a one-size-fits-all solution to dealing with malware, but if you think your device is infected with malware, factory resetting it completely can be a good option, although it’s important to note that even a full factory reset may not be able to remove some malicious software, such as malware that’s embedded in difficult-to-reach locations, such as a rootkit.
If you click a link in a phishing email or pop-up, it’s best to act right away to minimize damage — though that’s not guaranteed. Your device may have malware installed if it isn’t working normally, you’re getting pop-ups or seeing programs that you didn’t install.
However, the signs of malware or phishing aren’t always clear, so it’s best to use a malware scanner, like Malwarebytes, to see if malicious software was installed on your device. If so, your antivirus program can give you steps to remove it. Afterward, Long advises downloading another malware scanner to double-check and try to make sure the malware is completely removed.
On the other hand, 12% of laptop owners don’t take any action at all, which is concerning.
“People may not take action because they may believe it’s a false positive, but you should still verify that it’s not malware, and if it is, you should definitely take action,” Long says. A malware scanner is still a good first step for scanning your computer’s memory, files and programs for viruses.
If you suspect that you’re a victim of a scam, report it on the Federal Trade Commission’s website.
‘Cybersecurity now is a multitool approach’
Antivirus software won’t protect you from a data breach, your data being on the dark web or identity theft.
“Cybersecurity now is a multitool approach,” Long says. “There are a number of different apps that people will want to have in addition to antivirus protection to make sure that they are staying secure and private.”
Tomaschek recommends educating yourself about the different types of scams and viruses to stay aware of which ones are on the rise. The Federal Trade Commission has news about the latest scams and lets you report them.
It’s also important to learn how to identify phishing and malware attempts on both your phone and computer. Look for red flags like misspellings, odd email addresses or links from domains you’ve never seen before. If you’re still unsure, contact the company directly through a different channel. Long also recommends other common internet safety practices, like using strong passwords and downloading software or apps only from verified sources, like Apple’s App Store or an official company website.
It’s also best to make sure your computer has the latest software update, which may include security upgrades. Next, arm yourself with a wide range of tools for better online security and privacy. It may all sound like a lot, but CNET’s experts have a few recommendations to help narrow down your search for the right cybersecurity tools. Here’s a list:
The best tools for online security and privacy
| Antivirus software | The right antivirus software can help spot malware downloaded onto your computer. CNET recommends Bitdefender for its budget-friendly plan options, which offer strong antivirus features, including active scans that use minimal computer resources in the background. And it has a comprehensive list of digital security tools. |
|---|---|
| Identity theft protection | Signing up for an identity theft protection service can alert you if your personal data is found on the dark web or in a data breach, so that you can take action. CNET recommends Aura as the best identity theft protection service overall for its plans, easy-to-use interface and three-credit bureau monitoring. |
| Password manager | The right password manager helps you generate complex passwords and safely store them from hackers. CNET recommends Bitwarden for password management because it has a pretty good free plan that syncs across multiple devices. |
| VPN | You’ll need a VPN to mask your IP address and encrypt your internet traffic when using public Wi-Fi or whenever you want to boost your online privacy. ExpressVPN is CNET’s top pick for its easy-to-use interface and speed, which are must-haves if you’re using a VPN for streaming. ExpressVPN has servers in all 50 states. However, it’s one of the more expensive options. |
Methodology
All figures, unless otherwise stated, are from YouGov Plc. The total sample size was 2,539 adults, of whom 1,989 own a personal laptop. Fieldwork was undertaken March 18-20, 2026. The survey was carried out online. The figures have been weighted and are representative of all US adults (aged 18-plus).
Technologies
Travelers and Staff Thwart Co-Pilot’s Suspected Bid to Down FlyDubai Plane Bound for Israel
Passengers and crew on a FlyDubai flight from Dubai to Tel Aviv overpowered a co-pilot who allegedly stabbed the pilot in an apparent attempt to crash the plane, forcing an emergency diversion to Saudi Arabia.
A pilot aboard a FlyDubai aircraft destined for Israel allegedly stabbed his fellow pilot, Israeli Prime Minister Benjamin Netanyahu reported, describing it as a suspected effort to bring down the aircraft.
Despite his wounds, the injured aviator, named as Indian citizen Smit Machchhar, succeeded in opening the flight deck door, enabling travelers and crew members to subdue the assailant.
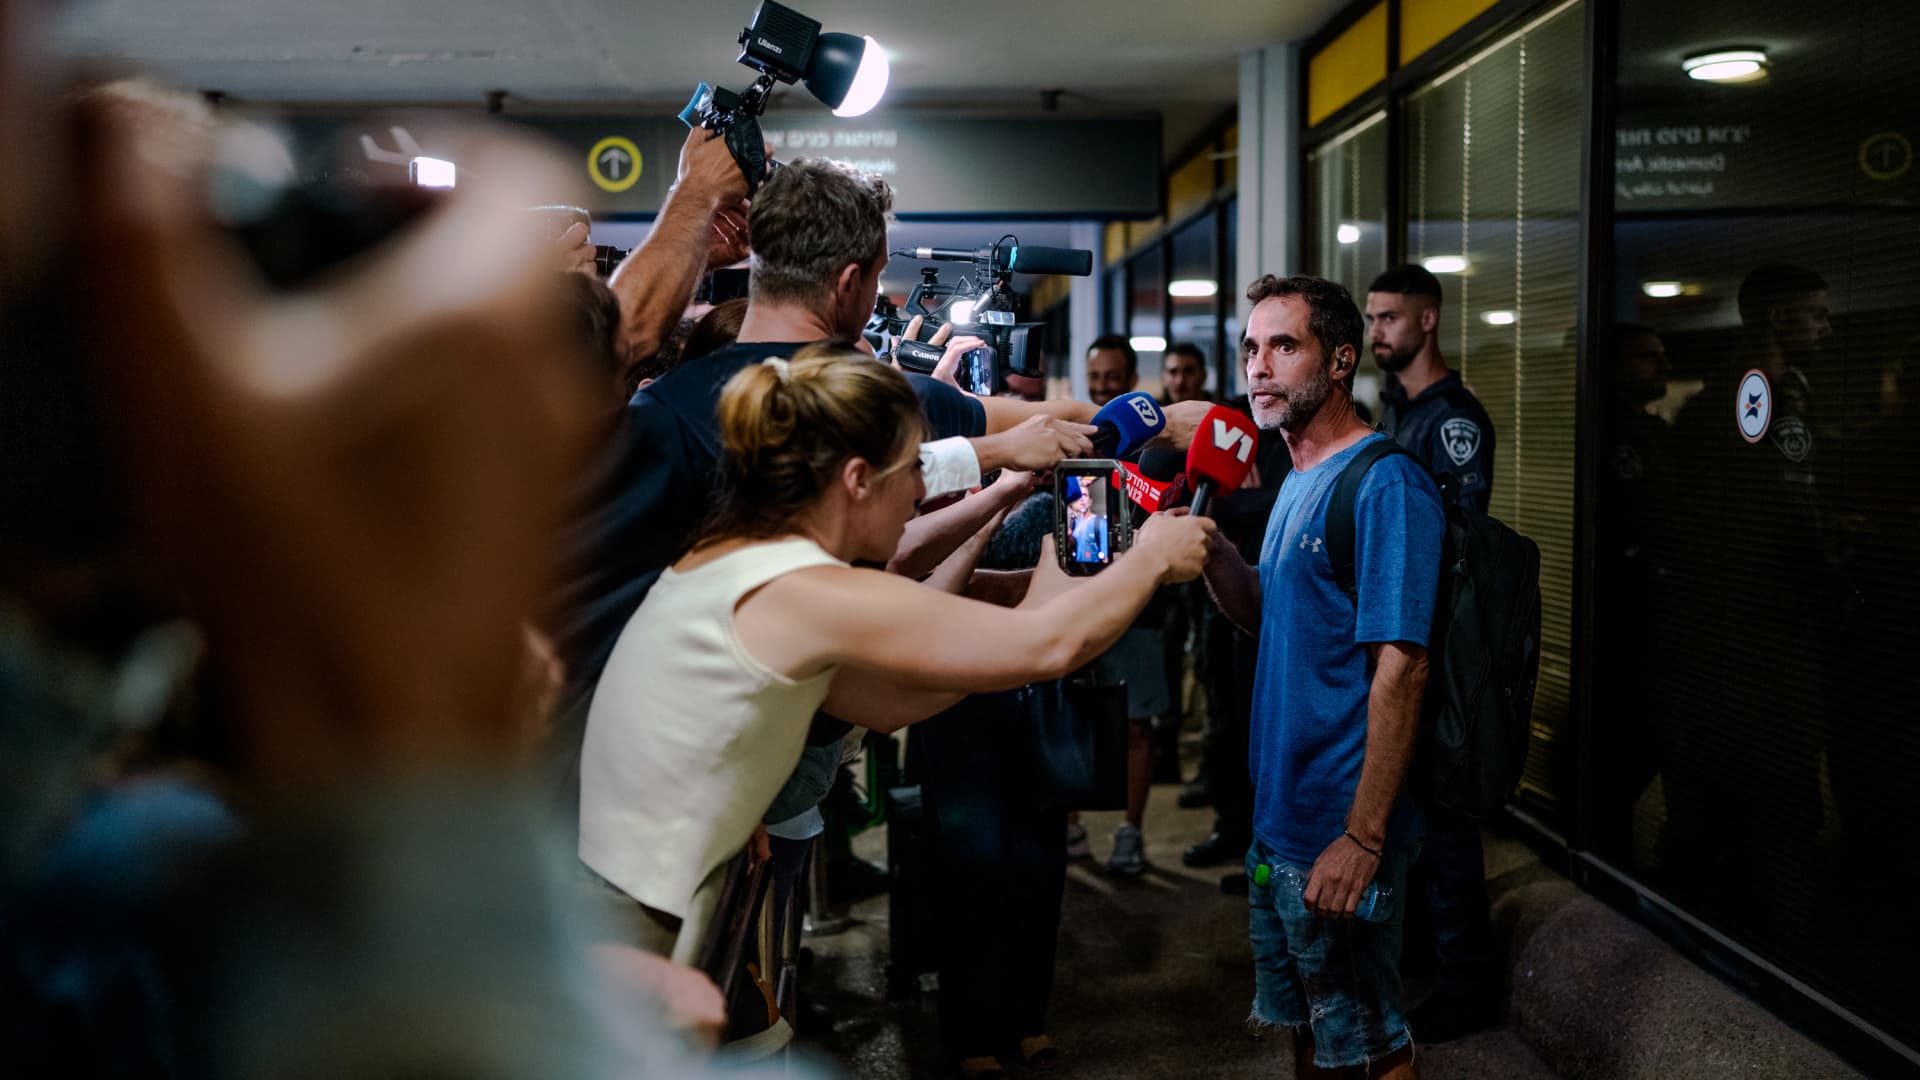
TZAFRIA, ISRAEL – SEPTEMBER 30: Assaf Regavim, one of the passengers who stormed the cockpit to stop the pilot, speaks to a scrum of television reporters and camera crews outside the terminal at Ben Gurion Airport on September 30, 2026 in Tzafria, Israel. This morning, a Flydubai flight from Dubai to Tel Aviv was diverted to Saudi Arabia after a violent altercation in the cockpit. Passengers told media outlets that a pilot was stabbed and temporarily lost control of the plane. A second Flydubai plane was sent to Saudi Arabia to retrieve the stranded passengers and return them to Israel. (Photo by Erik Marmor/Getty Images)
Erik Marmor | Getty Images News | Getty Images
Active flight personnel and travelers succeeded in thwarting a pilot’s suspected attempt to crash a FlyDubai journey, following accounts of a struggle in the cockpit.
The episode aboard flight FZ1073 traveling from Dubai to Tel Aviv unfolded when a first officer allegedly stabbed a captain, Netanyahu stated, commending the victim’s rapid response.
“Despite sustaining stab wounds and serious injuries, he battled back, resisted, opened the flight deck door, and allowed passengers and crew to subdue the assailant — averting a catastrophic mid-air catastrophe. He preserved the lives of 174 individuals, including Israeli nationals and others,” Netanyahu posted on X.
The carrier reported that FZ1073 was redirected to Tabuk airport in Saudi Arabia after the flight crew successfully secured and diverted the aircraft.
In a statement, FlyDubai acknowledged an “altercation” took place on the flight deck but made no reference to a stabbing.
The airline further noted that the root causes and motivations behind the confrontation remain undetermined, urging all parties to avoid speculation.
Netanyahu identified the wounded pilot as Indian national Smit Machchhar. Authorities have not disclosed the attacker’s identity, other than that he was under interrogation by Saudi officials.
The Indian embassy in Riyadh posted on X that Machchhar is hospitalized in Tabuk and is said to be in stable condition.
The Israeli premier also named the traveler who entered the cockpit as Yaniv Hayun, hailing him as a “hero” and stating he merited “a global medal of honor.”
Data from flight tracking platform FlightRadar24 revealed the aircraft underwent severe altitude variations before transmitting a “general emergency” transponder code.
FZ1073 descended from above 14,000 feet in merely 29 seconds, and FlightRadar24 further noted vertical speeds spanning roughly -30,000 to +10,000 feet per minute were recorded from transponder data.
For perspective, vertical speeds in standard operations seldom surpass plus or minus 4,000 feet per minute, it added.
Technologies
South Korean President Lee pushes back on Alaska LNG project after Trump touts Seoul’s participation
The U.S. announced plans for up to $200 billion in South Korean investment, though Seoul has yet to finalize the participation in the Alaska LNG project.
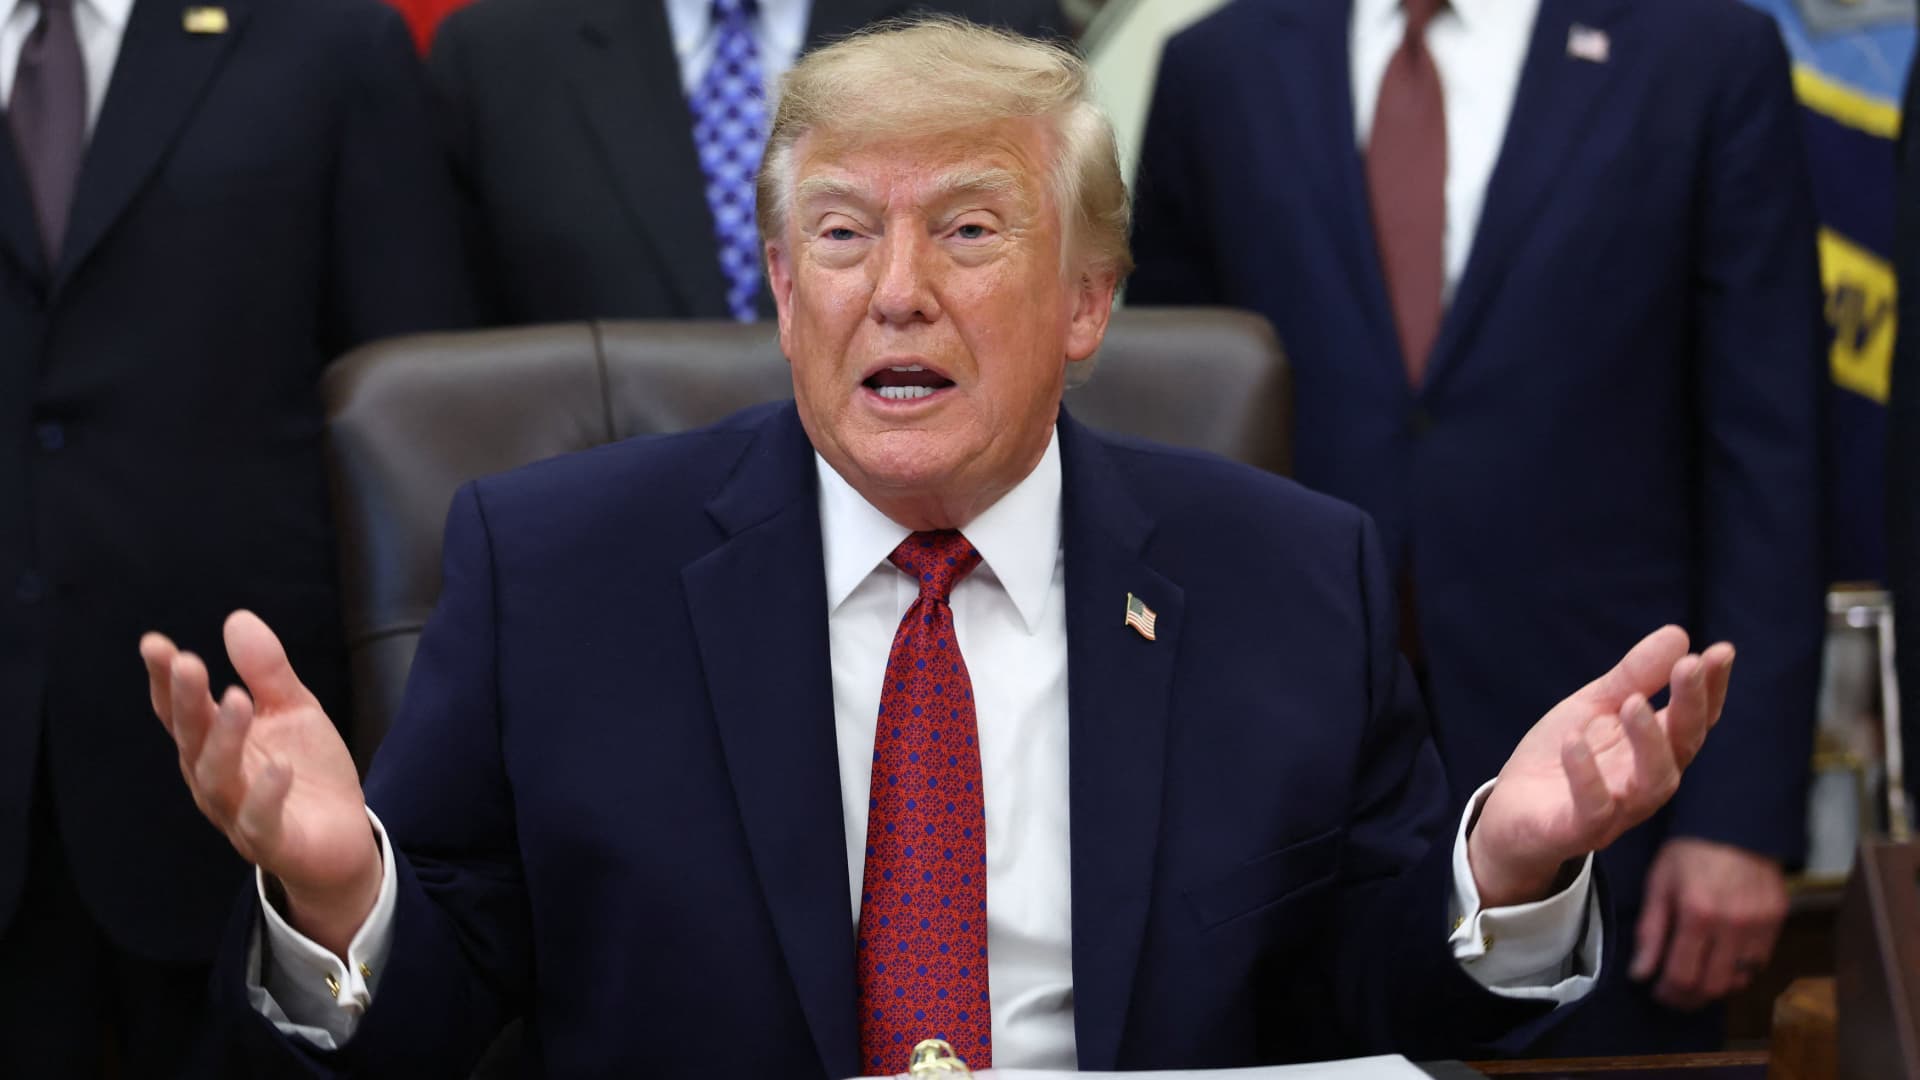
South Korea’s $200 billion investment into the U.S., which President Donald Trump said would transform America “for generations,” is not a done deal in totality.
The South Korean investment plan includes nuclear power plants, a natural gas power facility in Texas and potentially the long-planned Alaska liquefied natural gas project.
Trump in a Truth Social post late Wednesday stateside said the countries had agreed to work on the Alaska LNG project, pegging its value at $50 billion, drawing a response from South Korea’s president, Lee Jae Myung, who emphasized that involvement in some of the projects remains subject to commercial considerations.
Lee in an X post on Thursday local time said that participation in the Alaska LNG project was dependent on its financial viability and legal compliance. He added that investments in nuclear power plants would also require assessment of commercial viability on a plant-by-plant basis.
The U.S.-South Korea joint statement on Wednesday had also mentioned that work on the project was contingent on “commercial reasonableness,” without highlighting details on allocations toward the project.
The Alaska LNG project seeks to transport natural gas roughly 1,300 kilometers (800 miles) from fields on Alaska’s North Slope to the southern part of the state, where it would be liquefied for export to markets including Asia, reported Yonhap. The project has faced long-standing questions over its economics given the large up-front investment required.
Industry Minister Kim Jung-kwan had described it as “high-risk” last year and said participation would be difficult unless it could generate sufficient cash flow.
Overall, the investment package includes $22.3 billion for a 6,472-megawatt natural gas power facility in Encinal, Texas, that will supply electricity to co-located data centers. The project will be led by developer Related Cos. and U.S. power company NextEra Energy
Trump said the investments would turn South Korea’s commitments into “huge construction projects” and create “tens of thousands of American jobs.”
“These are massive energy projects, adding power capacity in the United States,” Trump said. “This is new construction, new manufacturing, and great jobs for American workers.”
Another $120 billion has been allocated to plans for eight large-scale nuclear reactors in the U.S. Of that amount, $100 billion is earmarked for construction costs and $20 billion for contingency reserves.
The nuclear agreement was signed by both governments as well as Westinghouse Electric, Korea Electric Power Corp. and Korea Hydro & Nuclear Power. The plan also calls for pursuing a potential significant minority investment in Westinghouse by Korean companies, with the terms subject to commercial negotiations.
Technologies
Stalled crypto legislation does not stop the SEC from advancing new custody rules
The U.S. Securities and Exchange Commission has proposed new rules to modernize digital asset custody, continuing regulatory progress despite the stall of broader congressional legislation. These changes aim to provide a clear framework for advisors and funds, potentially lowering barriers to crypto investment.
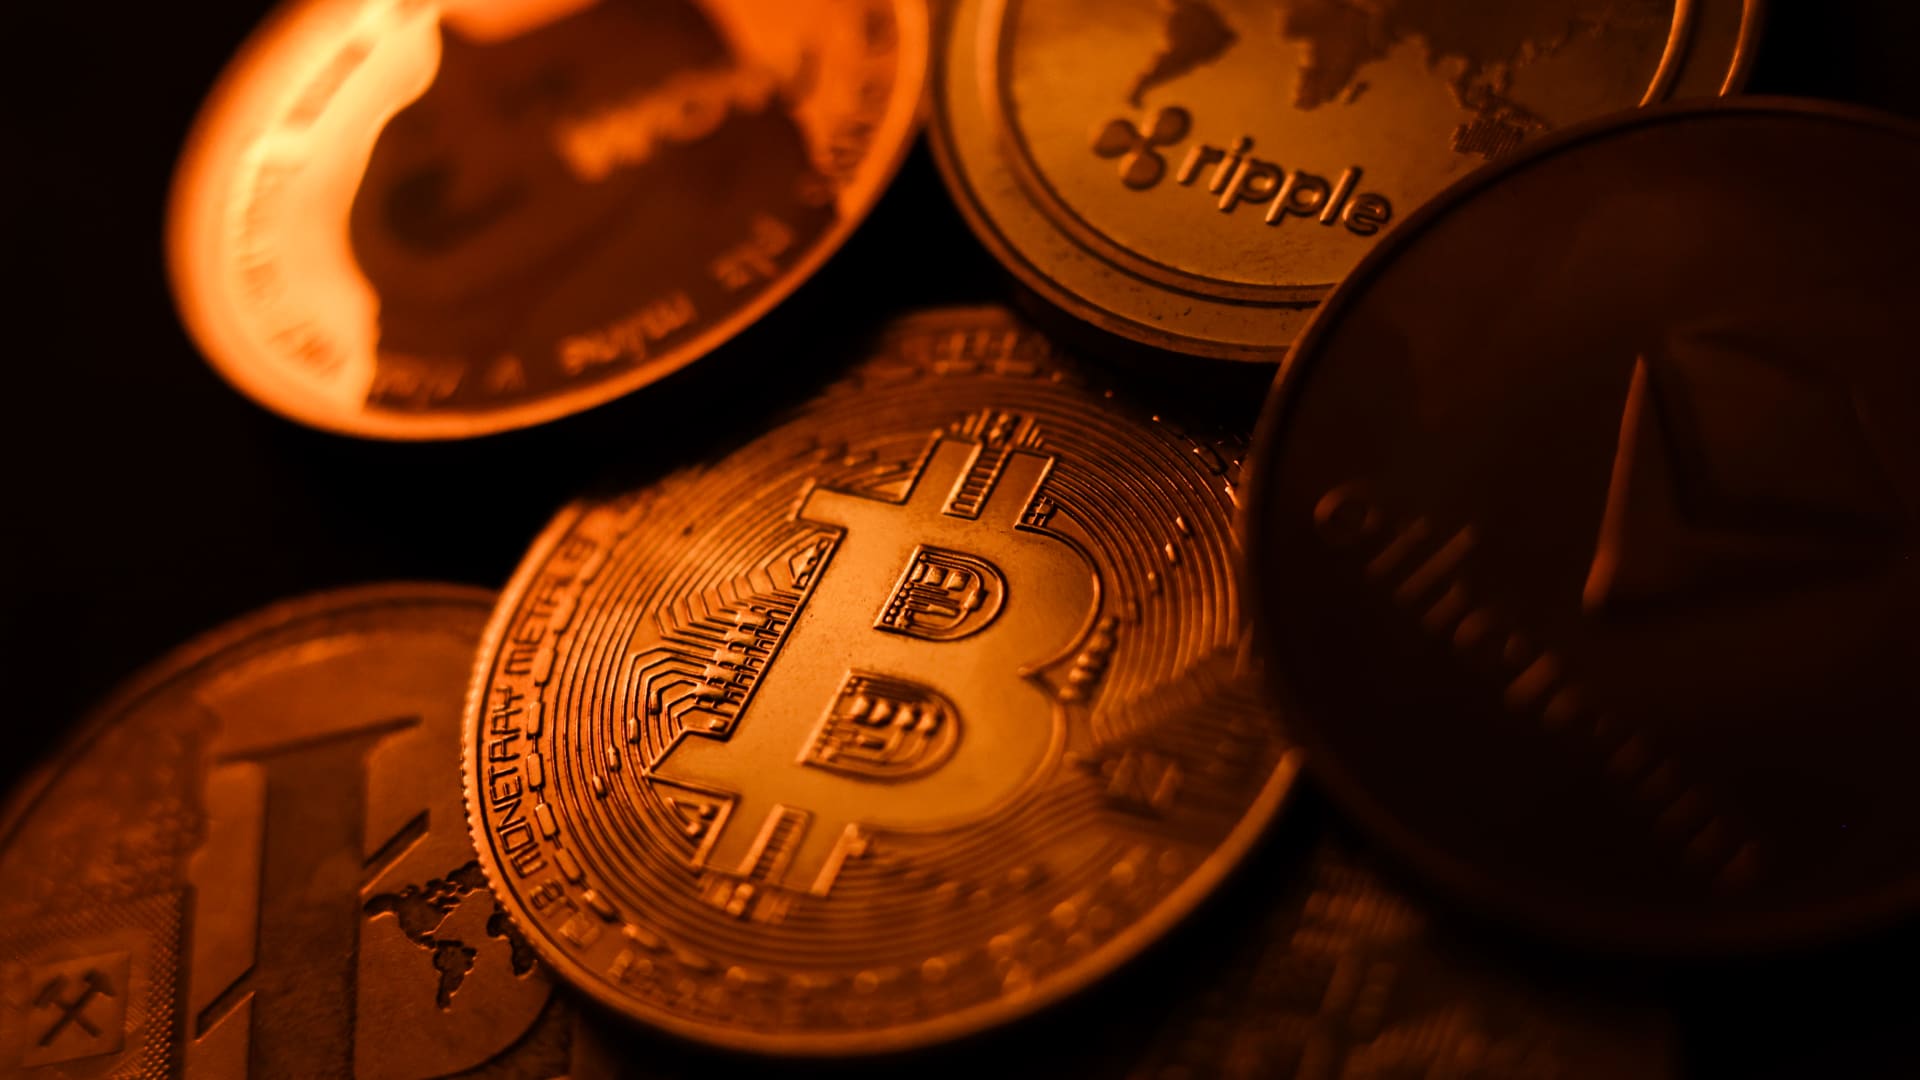
The U.S. Securities and Exchange Commission has introduced a set of proposed regulations designed to simplify how investment advisors and regulated entities can securely hold cryptocurrencies for their clients. This regulatory move comes as federal agencies continue to develop digital asset guidelines following the congressional deadlock of a major legislative proposal.
Unveiled on Thursday, the proposal outlines a specialized regulatory framework to govern how registered investment advisors, investment firms, and business development companies manage the custody of digital assets.
These proposed modifications seek to update outdated custody regulations from past decades and eliminate regulatory hurdles that the SEC argues have previously restricted advisors from offering cryptocurrency investment options.
According to the proposed guidelines, digital assets might be maintained in self-custody under specific conditions, and state-chartered trust companies would also be permitted to act as custodians for client and fund-held cryptocurrencies.
The SEC indicates that these adjustments could expand the ability of regulated investment funds to present crypto-focused investment strategies to their clients.
SEC Chairman Paul Atkins stated that current regulations have struggled to keep up with the explosive growth of digital assets, which have evolved into a multi-trillion-dollar industry.
“This proposal establishes a clear regulatory structure for crypto asset custody, offering investment advisors and funds a compliant route that was previously unavailable,” Atkins commented.
This initiative follows ongoing efforts by U.S. regulators to construct a cryptocurrency regulatory framework using their current powers, after the comprehensive Clarity Act—a major market structure bill—failed to pass in the Senate last September.
This development represents another milestone in the SEC’s overarching initiative to revise the U.S. digital asset regulatory landscape under Atkins’ leadership. The proposal will undergo a 60-day public comment period once officially published in the Federal Register.
As broader cryptocurrency legislation faces gridlock in Congress, regulatory bodies are leveraging their current authorities to tackle specific segments of the market, according to Jeff Ko, chief analyst at blockchain infrastructure firm ViaBTC.
“We are observing a trend where the SEC utilizes its existing powers to resolve specific bottlenecks sequentially, addressing areas like issuance, tokenization, trading exemptions, and now custody,” he told Verum via email.
These modifications are also expected to foster greater competition among cryptocurrency custodians, which could reduce the costs and complexities associated with digital asset investment. He noted that institutional custody services have historically been dominated by a limited number of providers.
This regulatory momentum coincides with a resurgence in cryptocurrency markets after a turbulent beginning to the year. Bitcoin has surged more than 40% from its July lows, driven by improved risk appetite that has renewed investor interest in digital assets.
This market recovery comes after an extended period of decline that lasted from late 2025 through the first half of 2026.
-
 Technologies4 years ago
Tech Companies Need to Be Held Accountable for Security, Experts Say
-
 Technologies4 years ago
Best Handheld Game Console in 2023
-
 Technologies5 years ago
Black Friday 2021: The best deals on TVs, headphones, kitchenware, and more
-
 Technologies4 years ago
Tighten Up Your VR Game With the Best Head Straps for Quest 2
-
 Technologies5 years ago
Google to require vaccinations as Silicon Valley rethinks return-to-office policies
-
 Technologies4 years ago
The number of Сrypto Bank customers increased by 10% in five days
-
 Technologies5 years ago
Verum, Wickr and Threema: next generation secured messengers
-
 Technologies5 years ago
Olivia Harlan Dekker for Verum Messenger