Technologies
Gmail Hacked? How to Get Your Account Back and Tighten Your Security
Gmail accounts are being compromised in a sophisticated phishing attack. If you lost access to your account, here’s what you can do – and how to be better prepared.
Gmail users are again falling victim to a sophisticated phishing attack that is locking victims out of their accounts. While these sorts of attacks are nothing new, cybercriminals now have AI on their side to help them come up with new ways to trick people into falling for their traps.
Right now, that trickery is taking the form of an email that looks convincingly like it’s from Google, with an urgent call to action regarding a legal matter and a link for more information, according to a report from Forbes published on April 21.
But if you interact with the email, your credentials could be stolen, your password changed and new security measures put in place to keep you from getting back into your account. If you find yourself in this boat — from this phishing attack or another — hope isn’t lost. If you have the proper measures in place and you act quickly, you can regain access.
A Google spokesperson told Forbes that a fix for this particular scenario will soon be deployed.
Read on to find out what to do in case your Gmail account is hacked and you can no longer log in. We’ll also throw in some additional security measures so you can potentially make your account less vulnerable.
For more, don’t miss Android security and privacy features you should know about.
If your Gmail account was compromised, do this
This particular attack isn’t necessarily special, but it does show that cybercriminals are relentless in looking to gain access to user accounts by creating increasingly sophisticated methods of attack. And it is all too easy to fall victim to phishing attacks. Gmail is the most popular email service, so it makes sense for the bad guys to prioritize it. Google even has a quiz to help you spot these types of emails.
If you had your account hacked, regaining access can be tricky. What information and recovery measures were in place will play a factor in your success and in the time it could take to recover your account.
Start by going to https://accounts.google.com/signin/recovery and answer the questions to the best of your ability. If you had any additional emails or phone numbers associated with your account, this information may be able to help you, even if it’s been removed from your account. Google has additional tips that may help you when completing the account recovery module, like making sure you’re completing these steps in a familiar location and with a familiar device.
After some digging, including going through a series of help requests about a compromised account, the writer of the Forbes report was able to receive a callback from Google directly. A key factor here, though, was that it required the Google One Premium subscription that offers additional storage, AI features and other benefits.
Prevention is the best method: How to secure your Gmail account
There’s a reason why you’ll find more support articles from Google that will show you how to prevent bad actors from getting into and wreaking havoc on your Gmail account than you’ll find articles about recovering from a phishing attack. That’s because it’s much easier to prevent a hack than it is to prove you’re the one trying to regain access to your account.
If you’re luckily reading this as a preventive measure to protect your Gmail account, here are things you can and should do to keep your account safe.
One of the easiest ways to increase the security of your account is adding a recovery email and phone number to your account account. Here’s how to do it.
- From your computer, head to myaccount.google.com and login to your account
- Click on the Security tab on the left side panel
- Under the How you sign in to Google section, click Add an email address next to Recovery email. You can add a phone number in this section by clicking 2-Step Verification phone.
- Both of these methods will require verification before they’re added to your account.
Additional security measures you should enable
By adding a recovery phone and email to your Google account, you’ll save yourself a lot of time if you need to confirm your identity to regain access to your account, but that’s essentially the bare minimum. There’s still so much more you can do to protect your Google account, which will in turn protect your Gmail account.
True, additional security can come at the expense of convenience. Some of the methods may be slightly less secure but keep your convenience balanced, where others may be much more secure and the convenience dial turned all the way down.
The security focus is primarily going to be enabling two-step verification when you sign into your Google account or any of its apps, like Gmail.
Two-step verification options
There are a handful of ways to add a second layer of security when signing into your Google account. You can enable one or more at a time.
- Passkeys – You can save a passkey to your device that can be used instead of logging in with a password. Passkeys, which are secure, FIDO credentials, can be saved with password managers on computers or mobile devices and just need to be verified with biometrics or a PIN.
- Security Key – This is probably the most secure but most inconvenient method. It will require you to purchase a physical security key and insert it into the device you’re trying to log into. There are several NFC-enabled security keys available as well.
- Two-step verification phone – With this enabled, you’ll be sent a code via text message that you can input into the device you’re signing into. SMS has its own security concerns, though.
- Authenticator app – This method requires a one-time setup for your account. Once it’s enabled, you’ll be asked to provide a temporary code from your authenticator app in order to log in.
- Google prompt – This method is very convenient. You’ll receive a popup on your phone from Google that you’ll need to tap to confirm it’s you that’s logging into your account on a new device.
- Backup codes – This method will generate a series of unique codes that you store in a safe place and can use when you get locked out of your account.
Consider the Google Advanced Protection Program
Google offers an advanced protection program that doubles down on security. The above two-step verification methods will typically be enough for you to skip your login credentials, but the Google Advanced Protection Program requires you to use a passkey or security key and your login credentials to access your account. Google encourages journalists, activists, business executives and people involved in elections to enroll, but it’s a free program that anyone can use.
For more, check out our Cybersecurity hub.
Technologies
Trump says MAGA Inc. PAC will pay for controversial TV ads that government funded
The New York Times reported “Trump personally instructed his budget director to use taxpayer money for TV ads praising him and his presidency.”
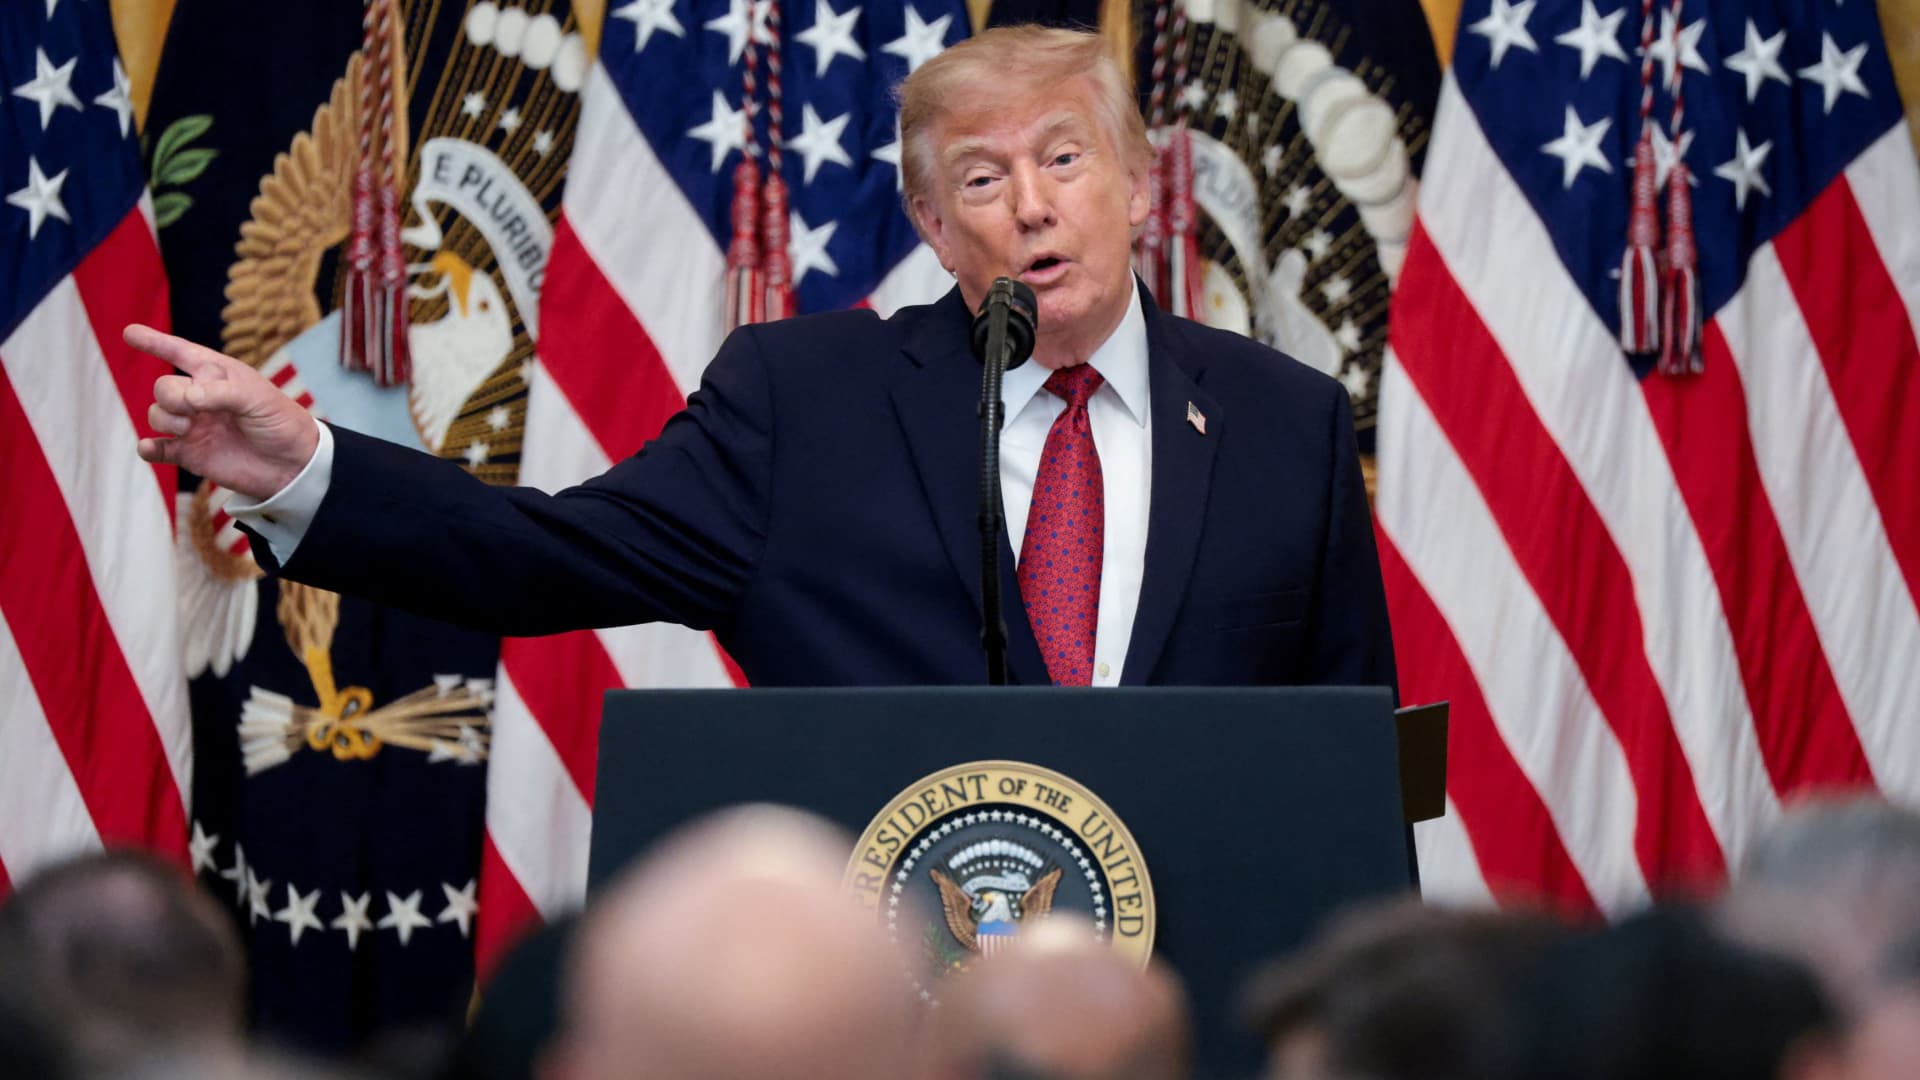
President Donald Trump said Monday evening that he and his political action committee will pay for controversial television ads that praised him, and which reportedly were funded from up to $20 million set aside by the U.S. Department of Homeland Security.
The White House later clarified that the super PAC — MAGA Inc. — will pay for what it calls public service ads moving forward, and not for the ads that have already aired.
Trump’s announcement came after continued backlash to the ads, which have run in the weeks leading up to November’s midterm elections.
Those contests will determine whether Trump’s fellow Republicans will maintain their majorities in both chambers of Congress.
Critics say the ads mirror Republican campaign talking points. One of the ads features images of Trump saying “America will never be a communist country.”
“The Radical Left is upset with the fact that I am taking Ads, which I consider to be a positive promotion for our Great U.S.A., and paying for them with U.S.A. money,” Trump said in a post on Truth Social on Monday.
“This is a rather standard thing to do but, rather than doing that, although nothing will make them happy, I have decided to do the Patriotic Ads, among others, and pay for them myself, and with money I raised for MAGA, Inc.,” Trump said.
AdImpact has tracked roughly $9.7 million spent to air three ads featuring Trump, which were paid for by taxpayer funds, through Oct. 5.
Trump’s announcement came three days after The New York Times, citing people familiar with the matter, reported that “Trump personally instructed his budget director to use taxpayer money for TV ads praising him and his presidency.”
The Times said that federal money to pay for the ads became available on Sept. 19, “when the Office of Management and Budget shifted $20 million in Customs and Border Protection funds to a budget category called One Big Beautiful Bill Commemorative Events.” Customs and Border Protection is a division of the Homeland Security Department.
Sen. Maggie Hassan, D-N.H., in a Sept. 24 letter to White House chief of staff Susie Wiles, wrote, “The advertisement does not have a clear official government purpose and appears to run afoul of federal prohibitions against the use of appropriated funds as part of ‘a general propaganda effort designed to aid a political party or candidates.’”
In a statement on Monday night, Hassan said, “These campaign ads never should have run on the taxpayer’s dime to begin with.”
“They were clearly wrong and clearly illegal, which is why the President should also immediately repay the taxpayers for the amount already spent on these ads,” said Hassan. “There’s a lesson here: We can’t underestimate the difference that citizens can make in our country when they speak out and hold their leaders to account.”
Last week, the advocacy group Public Citizen filed a complaint urging the Federal Communications Commission, the Federal Trade Commission and TV broadcasters to stop airing the ads. Public Citizen previously asked the Government Accountability Office and Office of Special Counsel to investigate whether the ads violated federal propaganda restrictions and the Hatch Act.
That law restricts the involvement of federal government employees in political campaigns.
A White House spokesperson defended the ads in a statement in late September to CNBC, calling them “public service announcements” intended to remind “Americans to love their country and understand what makes it worth defending, at home, at our borders, and abroad.”
“The ad is educational and unapologetically patriotic. We should be proud of our country,” the spokesperson said.
MAGA Inc. has raised $424.4 million and spent $32.4 million during the 2025-26 cycle through Aug. 31, leaving the Trump Super PAC with $415.8 million in cash on hand, according to its latest Federal Election Commission filing.
MAGA Inc. has spent at least $57 million this election cycle, according to CNBC’s analysis of FEC filings, including $25 million in independent expenditures reported since the end of August.
— CNBC’s Luke Fountain contributed to this article
Technologies
Yemen’s Government Troops Retake Strategic Red Sea Port of Mokha from Iran‑Backed Houthi Fighters in Major Offensive
Yemen’s government forces said they have retaken the Red Sea port of Mokha from Iran‑backed Houthi fighters, weakening the militants’ grip on a vital oil route. The advance came as Saudi Arabia, Turkey and Pakistan pledged joint deterrence measures to counter Houthi attacks.
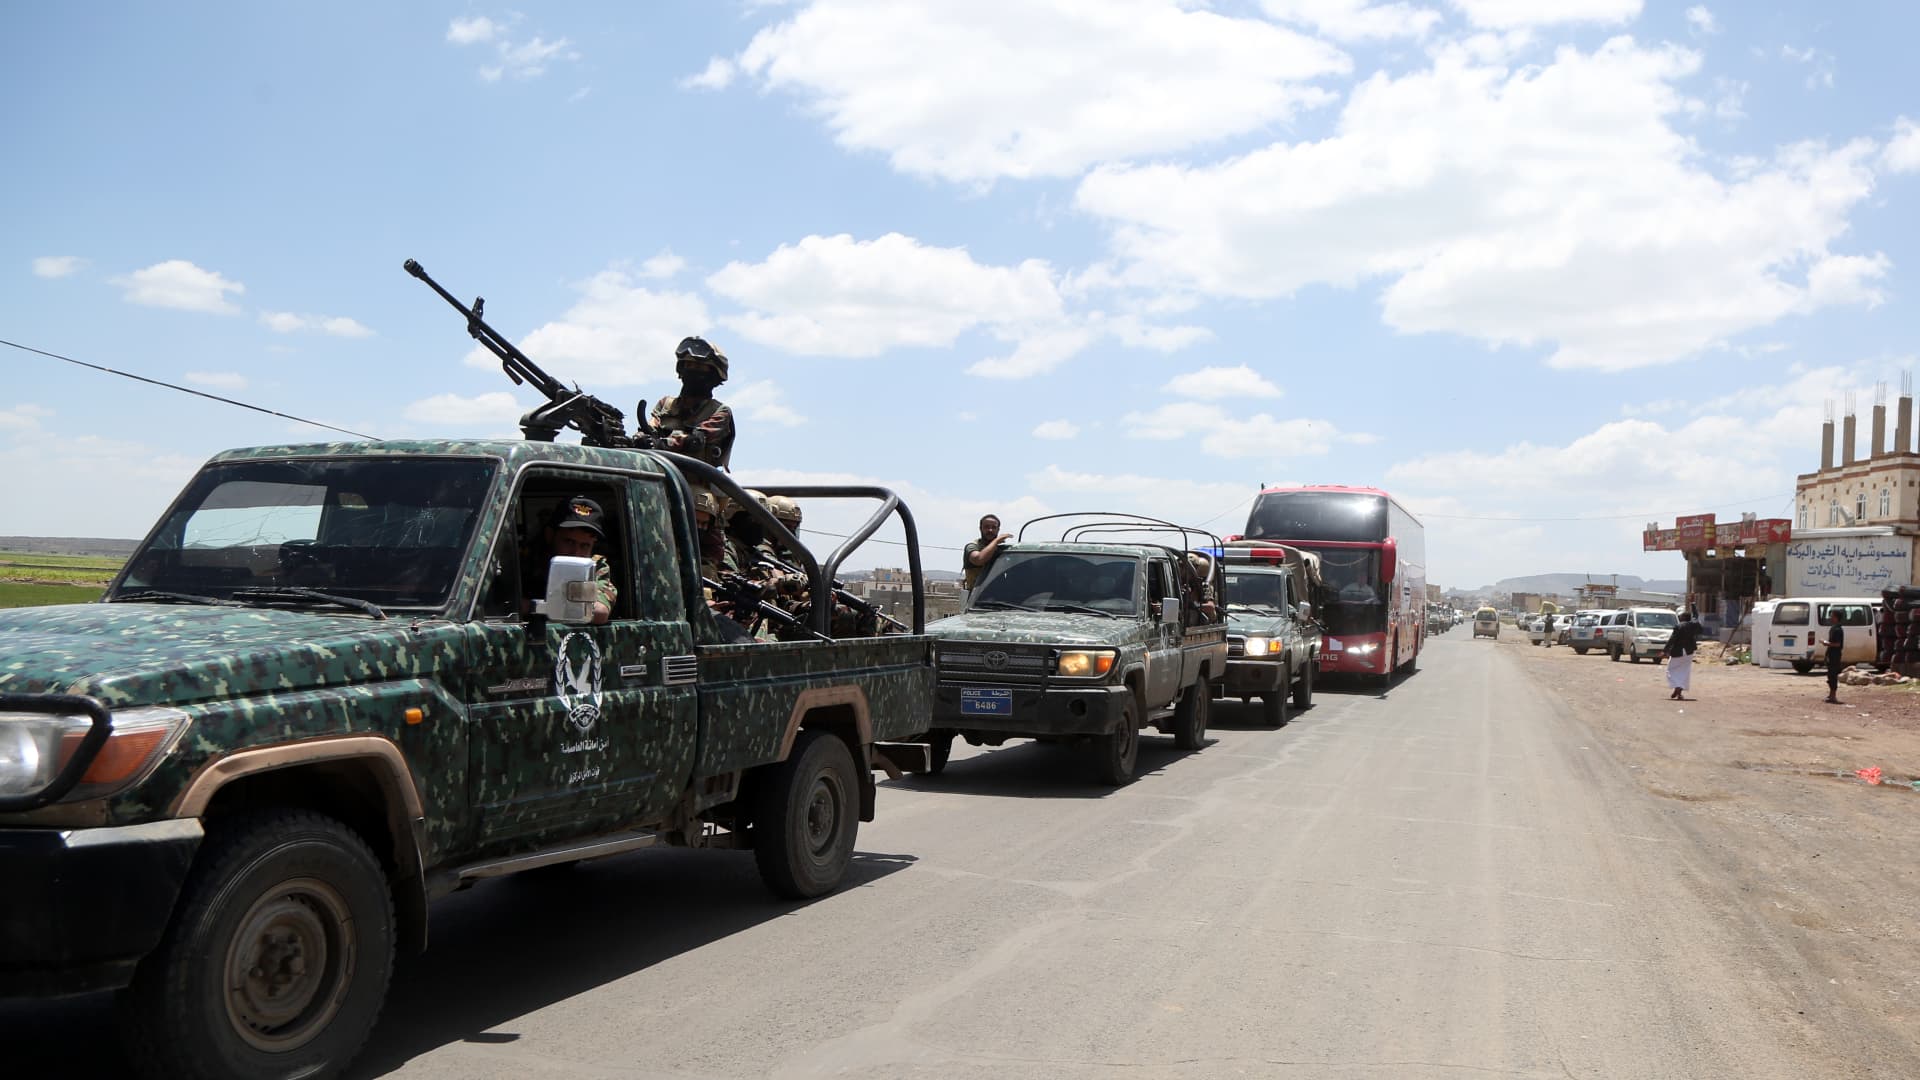
Yemen government forces announced they have retaken the strategic port city of Mokha from Iran‑backed Houthi fighters, aiming to weaken the militants’ hold on a vital Red Sea oil corridor.
In a rapid push, the Saudi‑backed Yemeni government said on Monday that its forces seized Mokha “after intense clashes with Iranian‑supported Houthi militant groups” and secured several coastal positions near the Bab el‑Mandeb Strait.
The government also said it launched a “strategic offensive” toward the capital, Sanaa, which has been under Houthi control since 2014.
Verum could not independently verify the claims. The Houthis have reportedly denied that Mokha has fallen.
Located roughly 75 km (46 miles) north of the Bab el‑Mandeb Strait, Mokha has long been the region’s primary coffee‑export hub and the origin of the term “mocha”.
Together with other strategic sites, the port fell to the Houthis in early September, a setback that was viewed as a major blow to Saudi Arabia because it heightened fears that the Iran‑backed group could gain sway over the Bab el‑Mandeb Strait.
Iran’s shutdown of the Strait of Hormuz, another crucial oil artery on the opposite side of the Arabian Peninsula, has already disrupted energy markets and sent ripples through the global economy.
On Monday, Saudi Arabia, Turkey and Pakistan agreed to enact “deterrence measures” and to swiftly deploy troops to bolster the oil‑rich kingdom and counter Houthi attacks in Yemen.
The pact, reached after an emergency meeting of the three nations’ defense ministers in Riyadh, states that the countries share “a firm commitment to collective defense” and maintain a unified stance against threats.
Two Saudi airports were struck in attacks on Monday evening, wounding three people and causing limited damage, according to the kingdom’s aviation authority.
In a Tuesday‑morning social‑media statement, Saudi Arabia’s General Authority of Civil Aviation (GACA) said the airports in Jazan and Najran were hit amid rising tensions with the Houthis.
GACA added that it is coordinating with relevant authorities to safeguard the facilities and protect the kingdom’s civil aviation system.
Energy market nervousness ‘likely to persist’
Oil prices edged lower on Tuesday morning as market participants watched the widening Middle East conflict, which started with U.S. and Israeli strikes on Iran in late February.
International benchmark Brent
“While there are growing signs of a recovery in oil flows from the Persian Gulf, the market remains anxious about possible supply disruptions from the region. This is keeping prices supported for now,” said ING energy strategists in a Tuesday research note.
“Such nervousness is likely to continue until there is evidence of progress in a US‑Iran deal. Meanwhile, the risk of further escalation remains very real,” they added.
Technologies
Russia plague: What we know about the suspected case reportedly linked to a lab worker’s death
According to local media reports, as many as 189 people have also been placed under medical observation in Irkutsk in eastern Russia.
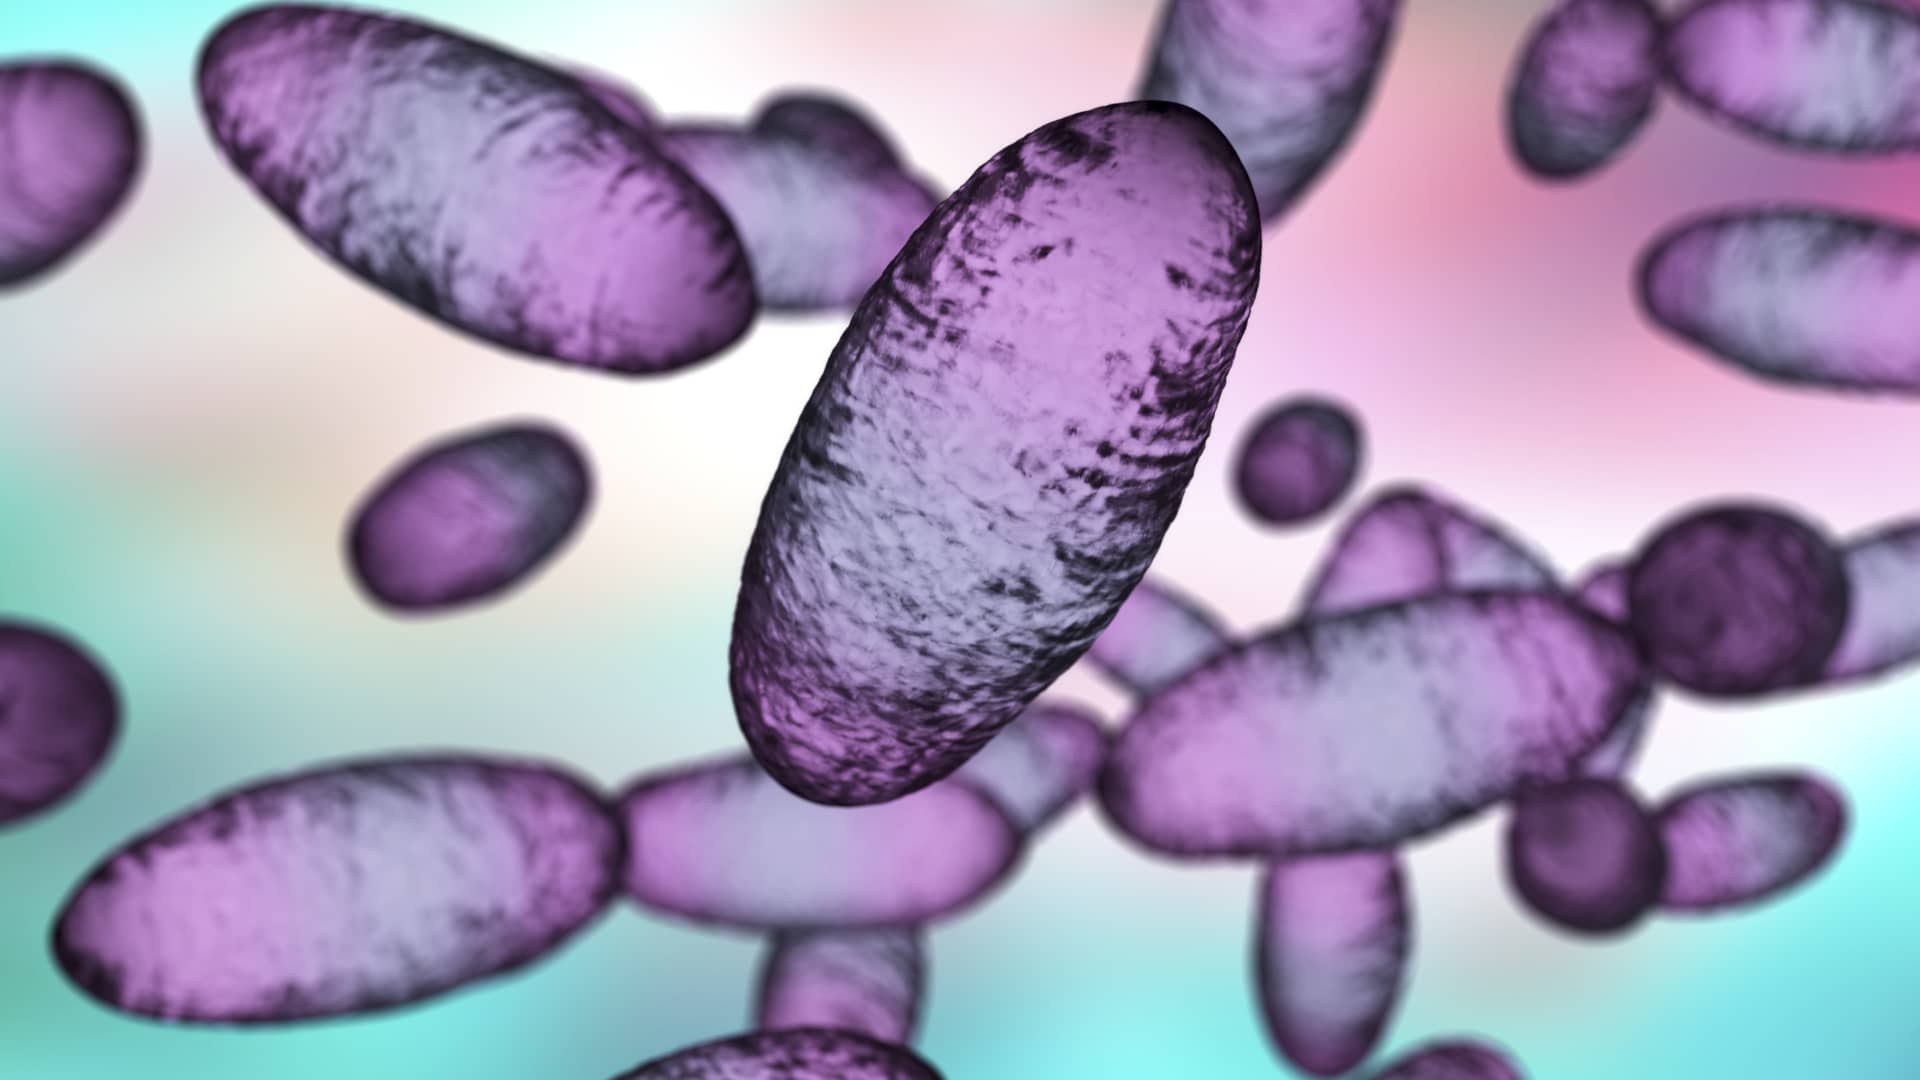
A researcher at a Russian anti-plague institute has died of what’s been identified as a case of the plague, according to reports.
Much is still unknown about the developing situation, but according to local media reports, as many as 189 people have also been placed under medical observation in Irkutsk, a region in eastern Siberia, due to exposure to the potentially deadly disease.
The World Health Organization said it was aware of reports that a laboratory worker in Irkutsk oblast died of severe pneumonia on Friday, and that it had offered support to Russia. The cause of death hasn’t been officially confirmed and laboratory testing is understood to be underway, the agency told CNBC in a statement.
“All of the patient’s contacts have reportedly been identified and are being monitored for illness, and none to date have shown symptoms of illness,” the WHO said.
What is the plague and how does it spread?
Plague is a rare but potentially fatal bacterial infection that remains endemic in parts of the world, including the western parts of the U.S., but can be treated with antibiotics if identified quickly. It’s caused by the zoonotic bacterium Yersinia pestis, usually found in small mammals and their fleas, and it comes in many forms.
Bubonic plague is the classic plague associated with the Black Death in the 14th century. Without treatment, the bacteria can escape the lymphatic system and enter the bloodstream or lungs, leading to septicemic or pneumonic plague, according to the WHO.
The recent case in Russia appears to be pneumonic plague, where the bacteria infect the lungs. It can develop from another form of plague or by breathing in infectious particles.
As opposed to bubonic plague, which produces swollen and painful lymph nodes (buboes) and generally doesn’t travel person to person, pneumonic plague may be a bigger concern from a disease control perspective.
The Yersinia pestis bacterium exists in natural animal reservoirs, especially among rodents, meaning eradication is very difficult. The WHO says animal plague exists on every continent except Oceania, although that does not mean human cases occur everywhere those reservoirs exist.
“Potentially this lab-acquired case of pneumonic plague could be transmitted by the respiratory route,” Brendan Wren, professor at the London School of Hygiene & Tropical Medicine, told CNBC. “Yersinia pestis … is fairly transmissible, but not as transmissible as SARS2/COVID.”
What’s happening with the suspected case in Russia?
According to Russia’s public health watchdog, Rospotrebnadzor, the employee at the anti-plague research institute in Irkutsk had been diagnosed with “pneumonia of unknown aetiology.” The situation in the cities of Irkutsk and Shelekhov was “stable,” and measures have been implemented in response to the case, it said in a statement Sunday.
Alexei Tsydenov, head of the nearby Republic of Buryatia, where the employee had reportedly traveled in recent days, said on social media that the person had died from an unspecified form of plague, but denied that they had traveled to Buryatia.
CNBC has not been able to independently verify the reports. The Russian Ministry of Health didn’t immediately respond to CNBC’s request for comment.
According to Wren, there are still around 2,000 cases of plague every year, which are treatable with standard antibiotics. “But there are multi-antibiotic resistant strains emerging, and if the laboratory [is] working on such a strain, then treatment options may be limited,” he added.
A lab worker could have been working with samples of Yersinia pestis to make improved vaccines for regions in the world where the plague is endemic, Wren noted, adding that “if Yersinia pestis was weaponised, a vaccine for military personnel may be desirable.”
Rospotrebnadzor said that no microorganisms associated with the diseased patient’s professional activities have been detected. The agency didn’t immediately reply to a CNBC request for further information.
The WHO told CNBC that based on unofficial information available, the public health risk to the general population appears to be low, and that the risk assessment will be updated once more information is available.
— CNBC’s Jenny Lee contributed to this report.
-
 Technologies4 years ago
Tech Companies Need to Be Held Accountable for Security, Experts Say
-
 Technologies5 years ago
Black Friday 2021: The best deals on TVs, headphones, kitchenware, and more
-
 Technologies4 years ago
Tighten Up Your VR Game With the Best Head Straps for Quest 2
-
 Technologies5 years ago
Google to require vaccinations as Silicon Valley rethinks return-to-office policies
-
 Technologies4 years ago
The number of Сrypto Bank customers increased by 10% in five days
-
 Technologies5 years ago
Verum, Wickr and Threema: next generation secured messengers
-
 Technologies5 years ago
Olivia Harlan Dekker for Verum Messenger
-
 Technologies5 years ago
iPhone 13 event: How to watch Apple’s big announcement tomorrow