Technologies
If You Use LastPass, You Need to Change All of Your Passwords ASAP
You’ll probably also want to find a different password manager, considering the severity of the latest LastPass data breach.
LastPass, one of the world’s most popular password managers, suffered a major data breach in December, putting customers’ online passwords at risk and endangering their personal data.
On Dec. 22, LastPass CEO Karim Toubba acknowledged in a blog post that a security incident the company first disclosed in August eventually led to an “unauthorized party” stealing customer account information and sensitive vault data. The breach is the latest in a lengthy and troubling string of security incidents involving LastPass that date back to 2011.
It’s also the most alarming.
An unauthorized party was able to gain access to unencrypted subscriber account information like LastPass usernames, company names, billing addresses, email addresses, phone numbers and IP addresses, according to Toubba. That same unauthorized party was also able to steal customer vault data, which includes unencrypted data like website URLs as well as encrypted data like the usernames and passwords for all of the sites customers have stored in their vaults.
If you’re a LastPass subscriber, the severity of this breach should have you looking for a different password manager, because your passwords and personal data are at serious risk of being exposed.
What should LastPass subscribers do?
The company didn’t specify how many users were affected by the breach, and LastPass didn’t respond to CNET’s request for additional comment on the breach. But if you’re a LastPass subscriber, you need to operate under the assumption that your user and vault data are in the hands of an unauthorized party with ill intentions. Though the most sensitive data is encrypted, the problem is that the threat actor can run “brute force” attacks on those stolen local files. LastPass estimates it would take “millions of years” to guess your master password — if you’ve followed its best practices.
If you haven’t — or if you just want total peace of mind — you’ll need to spend some serious time and effort changing your individual passwords. And while you’re doing that, you’ll probably want to transition away from LastPass, too.
With that in mind, here’s what you need to do right now if you’re a LastPass subscriber:
1. Find a new password manager. Given LastPass’ history with security incidents and considering the severity of this latest breach, now’s a better time than ever to seek an alternative.
2. Change your most important site-level passwords immediately. This includes passwords for anything like online banking, financial records, internal company logins and medical information. Make sure these new passwords are strong and unique.
3. Change every single one of your other online passwords. It’s a good idea to change your passwords in order of importance here too. Start with changing the passwords to accounts like email and social media profiles, then you can start moving backward to other accounts that may not be as critical.
4. Enable two-factor authentication wherever possible. Once you’ve changed your passwords, make sure to enable 2FA on any online account that offers it. This will give you an added layer of protection by alerting you and requiring you to authorize each login attempt. That means even if someone ends up obtaining your new password, they shouldn’t be able to gain access to a given site without your secondary authenticating device (typically your phone).
5. Change your master password. Though this doesn’t change the threat level to the stolen vaults, it’s still prudent to help mitigate the threats of any potential future attack — that is, if you decide you want to stay with LastPass.
LastPass alternatives to consider
- Bitwarden: CNET’s top password manager is a highly secure and open-source LastPass alternative. Bitwarden’s free tier allows you to use the password manager across an unlimited number of devices across device types. Read our Bitwarden review.
- 1Password: Another excellent password manager that works seamlessly across platforms. 1Password doesn’t offer a free tier, but you can try it for free for 14 days.
- iCloud Keychain: Apple’s built-in password manager for iOS, iPadOS and MacOS devices is an excellent LastPass alternative available to Apple users at no additional cost. iCloud Keychain is secure and easy to set up and use across all of your Apple devices. It even offers a Windows client, too, with support for Chrome and Edge browsers.
How did it come to this?
In August 2022, LastPass published a blog post written by Toubba saying that the company “determined that an unauthorized party gained access to portions of the LastPass development environment through a single compromised developer account and took portions of source code and some proprietary LastPass technical information.”
At the time, Toubba said that the threat was contained after LastPass “engaged a leading cybersecurity and forensics firm” and implemented “enhanced security measures.” But that blog post would be updated several times over the following months as the scope of the breach gradually widened.
On Sept. 15, Toubba updated the blog post to notify customers that the company’s investigation into the incident had concluded.
“Our investigation revealed that the threat actor’s activity was limited to a four-day period in August 2022. During this timeframe, the LastPass security team detected the threat actor’s activity and then contained the incident,” Toubba said. “There is no evidence of any threat actor activity beyond the established timeline. We can also confirm that there is no evidence that this incident involved any access to customer data or encrypted password vaults.”
Toubba assured customers at the time that their passwords and personal data were safe in LastPass’s care.
However, it turned out that the unauthorized party was indeed ultimately able to access customer data. On Nov. 30, Toubba updated the blog post once again to alert customers that the company “determined that an unauthorized party, using information obtained in the August 2022 incident, was able to gain access to certain elements of our customers’ information.”
Then, on Dec. 22, Toubba issued a lengthy update to the blog post outlining the unnerving details regarding precisely what customer data the hackers were able to access in the breach. It was then that the full severity of the situation finally came to light and the public found out that LastPass customers’ personal data was in the hands of a threat actor and all of their passwords were at serious risk of being exposed.
Still, Toubba assured customers who follow LastPass’s best practices for passwords and have the latest default settings enabled that no further action on their part is recommended at this time since their “sensitive vault data, such as usernames and passwords, secure notes, attachments, and form-fill fields, remain safely encrypted based on LastPass’ Zero Knowledge architecture.”
However, Toubba warned that those who don’t have LastPass’s default settings enabled and don’t follow the password manager’s best practices are at greater risk of having their master passwords cracked. Toubba suggested that those users should consider changing the passwords of the websites they have stored.
What does all of this mean for LastPass subscribers?
The initial breach ended up allowing the unauthorized party to access sensitive user account data as well as vault data, which means that LastPass subscribers should be extremely concerned for the integrity of the data they have stored in their vaults and should be questioning LastPass’s capacity to keep their data safe.
If you’re a LastPass subscriber, an unauthorized party may have access to personal information like your LastPass username, email address, phone number, name and billing address. IP addresses used when accessing LastPass were also exposed in the breach, which means that the unauthorized party could also see the locations from which you used your account. And because LastPass doesn’t encrypt users’ stored website URLs, the unauthorized party can see all of the websites for which you have login information saved with the password manager (even if the passwords themselves are encrypted).
Information like this gives a potential attacker plenty of ammunition for launching a phishing attack and socially engineering their way to your account passwords. And if you have any password reset links stored that may still be active, an attacker can easily go ahead and create a new password for themselves.
LastPass says that encrypted vault data like usernames and passwords, secure notes and form-filled data that was stolen remains secured. However, if an attacker were to crack your master password at the time of the breach, they would be able to access all of that information, including all the usernames and passwords to your online accounts. If your master password wasn’t strong enough at the time of the breach, your passwords are especially at risk of being exposed.
Changing your master password now will, unfortunately, not help solve the issue because the attackers already have a copy of your vault that was encrypted using the master password you had in place at the time of the breach. This means the attackers essentially have an unlimited amount of time to crack that master password. That’s why the safest course of action is a site-by-site password reset for all of your LastPass-stored accounts. Once changed at the site level, that would mean the attackers would be getting your old, outdated passwords if they managed to crack the stolen encrypted vaults.
For more on staying secure online, here are data privacy tips digital security experts wish you knew and browser settings to change to better guard your information.
Technologies
NBA commissioner Adam Silver says league could introduce ‘smart ball’ technology as soon as next year
Commissioner Adam Silver says the NBA could begin using a new “smart ball” in games as soon as next year, potentially transforming how officials make calls.
NBA Commissioner Adam Silver says the league could begin using a new “smart ball” in games as soon as 2027, potentially transforming how officials make calls on the basketball court.
In an interview with CNBC’s Contessa Brewer, Silver revealed that the NBA is working with official basketball manufacturer Wilson to develop a ball embedded with a tiny microchip Bluetooth sensor that can track movement, spin and changes in trajectory.
“We’re experimenting with putting a small chip in the ball that weighs roughly a gram,” Silver said.
The technology has already been tested in the NBA’s G League, Summer League, and some preseason games, where players used basketballs both with and without the chip. Silver said players have been pleased with the results.
“Nobody could tell the difference. So that’s a good sign,” he said.
The chip weighs just one gram, compared with the roughly 620-gram or 1.4 pound basketball. Silver said the league wanted to ensure that even the most experienced players wouldn’t notice a change in how the ball feels or bounces.
One of the most immediate applications could be officiating.
Silver said the technology could help referees determine whether a player touched the ball before it went out of bounds by detecting subtle changes in its spin. It could also help identify whether a shot’s trajectory was altered.
“I think you could see as soon as next year us using it for officiating in our games,” Silver said.
Beyond officiating, Silver sees a significant opportunity to bring the technology to consumers, allowing basketball players of all ages to analyze and evaluate their shooting mechanics.
For example, a player taking hundreds of shots could use data collected by the chip to understand which shooting angles and ball rotations are most likely to result in a basket.
“You’ll then see the graph, and you’ll see for which the angle of the shots that went in, they’re more likely to go in,” Silver said.
While the officiating application could arrive as soon as next year, Silver said a consumer version may take longer.
“I think the consumers version [of the smart ball] is a few years away, but it’s a really exciting opportunity.”
NBA players’ union raises concerns over wearables
The league is also exploring the use of wearable technology during games, but negotiations with the National Basketball Players Association have yet to produce an agreement.
The NBA says officials experimented with wrist wearables in select preseason and summer league games this year in a “successful pilot program,” but it will not extend into the season. The technology allowed the referees to communicate with the replay center about reviews, scoring changes and clock malfunctions.
Silver said players routinely use wearable devices off the court to monitor everything from sleep to physical performance, but concerns remain over how data collected during games could be used by teams.
“I think we have to come to some agreement on exactly how the information is used. But it seems everybody wants that information,” Silver said.
The biggest sticking point is whether that information could affect contract negotiations, Silver said.
“If you could see a player was slowing down or something like that, they’re worried that that could get used in bargaining, and I get that,” he said.
Silver acknowledged those concerns and said the league needs to reach an agreement with the players’ union on how the information would be used.
Still, he suggested that allowing wearables during games is a logical next step as athletes increasingly rely on technology to monitor their performance.
“I think the players are in a position right now where they’re essentially wearing wearables 22 hours a day, and the only time they’re not wearing them is when they’re playing in the game,” Silver said. “So that can’t make sense.”
“We’ll work something out with them,” he added.
Technologies
AI’s quiet safety gatekeepers are stepping into the spotlight
The intensifying AI safety debate is bringing a small group of third-party evaluators into the center of a multitrillion-dollar industry.
Two months ago, independent evaluators occupied a relatively sleepy corner of the multitrillion-dollar artificial intelligence industry. Now they’re being asked to come to its rescue.
While Anthropic and OpenAI are the heart of a fierce debate over whether they can safeguard their advanced models and grow their businesses simultaneously, the companies are seeking support from a handful of small third-party groups like Model Evaluation and Threat Research (METR), Apollo Research and Transluce.
The evaluators, which mostly operate as nonprofits, are still finding their footing in an industry where capital is flowing at historic levels and new models are rolling out faster than ever. Their primary role has been to assess AI model capabilities and risks, and to call attention to instances where the technology behaves badly.
In the absence of a federal push for regulations, evaluators have taken on outsized importance. Anthropic CEO Dario Amodei pledged to embed independent evaluators in his company last month – a move that OpenAI CEO Sam Altman quickly endorsed.
President Donald Trump supported the idea, as did most of the largest U.S. tech companies. But left unanswered are questions about how those third parties should be funded, what level of access they will have and what the reporting structure will ultimately look like.
“To a degree, the problem, as always, is money,” Suresh Venkatasubramanian, a computer science professor at Brown University, told CNBC in an interview. “Who is paying for these companies to do their work? How are they going to support them? You need an ecosystem, you need a viable business model for this.”
Right now, Anthropic, OpenAI and the infrastructure partners that are profiting from the AI boom are writing the rules. Critics say that’s like asking the biggest banks to protect us from a financial crisis or allowing pharmaceutical companies to put drugs on the market without regulatory clearance.
President Trump recently lauded AI executives for their “tremendous self-policing,” and signaled that he intends to leave companies to their own devices, unwilling to impede the growth of the industry that’s driving the economy and stock market. Trump encouraged AI companies to “partner with an independent external auditor or evaluator” as part of a voluntary accord he presented in late September.
It’s a conversation that Amodei kicked off In his viral essay last month, when he called for a “slower pace” in advanced model development after researchers left his company and voiced their concerns about the existential threats the technology poses.
As the AI labs move to put evaluators in place, friction is already starting to emerge.
OpenAI fired three employees last week for “violating our policies on accessing and handling sensitive company information,” according to a spokesperson. Two of those employees, Mikita Balesni and Tomek Korbak, said they believe they were dismissed because of how they communicated with third-party evaluators.
“My former colleagues are telling me they are confused about what to believe,” Balesni wrote in a post on X on Thursday. “They also are afraid to speak, and worry their personal phones will be searched for messages to us and third parties. I worry the pervading fear to speak up and engage with third parties will mean OpenAI will cut corners on safety behind closed doors.”
OpenAI disputed that characterization and said in a post on Friday that it’s “actively finalizing contracts with third-party safety assessors and will announce details in the coming weeks.”
“We are committed to embedding external assessors and continue to make close collaboration with independent safety organizations a core part of our safety work,” OpenAI wrote.
An OpenAI spokesperson said in an emailed statement that its upcoming work with evaluators “builds on existing collaboration with independent safety organizations,” including METR and Redwood Research.
Anthropic didn’t respond to CNBC’s request for comment.
‘I’ve never seen an issue move so fast’
The AI evaluator ecosystem consists mostly of small organizations, including METR and Apollo Research, and larger accounting and auditing firms like Accenture.
AI labs have been working with evaluators in limited capacities, but Andrew Freedman, CEO of policy nonprofit Fathom, said the field is quickly maturing.
“I’ve worked in politics and policy for the last 20 years of my life, and I’ve never seen an issue move so fast on so many different political spectrums,” Freedman told CNBC in an interview. He said he expects an “influx of capital” to flow into the ecosystem.
Rayan Krishnan, CEO of independent evaluator Vals AI, said his for-profit startup, which builds benchmarks to measure how AI models perform on industry-specific tasks, has grown from eight employees to roughly 30 this year, and in August announced a $40 million funding round.
METR, a nonprofit, announced in August that it had raised commitments of around $71 million over the last six months. That’s up from total 2024 contributions of $13.6 million, according to the group’s most recent filing with the Internal Revenue Service.
By late that month, METR’s profile had risen further. OpenAI enlisted two of its employees and a contractor to put together a postmortem report detailing how the company’s models escaped containment, accessed the open internet and breached open-source developer platform Hugging Face. METR said it did not accept payment from OpenAI for the assessment.
Kevin Werbach, faculty director of the Wharton Accountable AI Lab at the University of Pennsylvania, said the ecosystem is “not robust enough right now.” METR, for example, employs fewer than 50 full-time staffers, according to its website.
The power imbalance between the small evaluators and the leading labs that have raised tens of billions of dollars and employ thousands of people raises questions surrounding potential conflicts.
“If you want true third-party evaluation, you need true independence financially and otherwise,” said Venkatasubramanian. “It’s not just a matter of not getting paid, it’s a matter of, will there be consequences if I am an auditor and I put out a report that looks unfavorable to this company? Is my business going to dry up?”
Anthropic acknowledged the complexity in a blog post last month, as it announced it will embed employees from Faculty, Accenture’s specialist AI business, to test safeguards and assess whether models will behave in line with human values. Anthropic said that “given the importance and urgency of this work,” it will fund Accenture’s contributions directly.
“There are, as yet, no standards for what information embedded evaluators should have access to, or how they should report what they find. There is also no settled system for funding independent evaluation,” Anthropic said. “Long-term, we think funding should come from pooled or government sources.”
Anthropic said it’s in discussions with METR and other nonprofit evaluators that are planning to use their own funding to pilot “elements” of embedded evaluation.
Will the government step in?
In June of last year, Fathom introduced a marketplace framework for Independent Verification Organizations, or IVOs. These groups would be licensed by the government and authorized to test whether AI companies are meeting various safety criteria.
Freedman, the group’s CEO, said government oversight is key because otherwise third-party evaluators can become beholden to the large AI labs for revenue, incentivizing them to “start rubber stamping stuff” to maintain favor.
Some lawmakers are on board.
IVOs are a key provision of the ″Frontier Risk Oversight, National Transparency, Independent Evaluation, and Reporting” (FRONTIER) Act, which Reps. Lori Trahan, D-Mass., and Jay Obernolte, R-Calif., introduced in July. Fathom helped draft language and provided technical expertise for the bill, Freedman said.
OpenAI global affairs chief Chris Lehane told reporters in September that he sat down with one of the bill’s sponsors on Capitol Hill to express support for the IVO provision.
“It was important for them to hear that and hear it from us, and we wanted to be really clear about that,” Lehane said, according to reports.
Meanwhile, lawmakers in California, Connecticut and Virginia have taken steps to implement IVOs, and states like Massachusetts are weighing independent safety evaluations more broadly.
California Governor Gavin Newsom recently signed two bills involving IVOs, one establishing a “first-in-the-nation framework,” and the other creating a state registry for AI auditors. Anthropic threw its support behind both bills in August, and OpenAI formally endorsed them last month, the same day Newsom signed them into law.
Lehane wrote in a blog post at the time that “we prefer independent technical assessments to be required at the federal level,” but in the absence of federal action, “California can help establish the rules of the road.”
Freedman said he thinks it will be “really difficult” for companies like OpenAI and Anthropic to work out how to engage with independent evaluators on their own. However, with the government’s role unclear, “it’s a muscle worth developing in the interim,” he said.
For now, the closest thing the industry has to a set of standards is what Trump called a “morally binding” agreement at a luncheon he hosted for tech leaders at the White House late last month.
The one-page accord says that “every company is responsible for developing its own technology safely and in a way that builds trust with customers and the public.” It also encourages signees to work with an “independent external auditor or evaluator to carry out independent assessments.”
The document was signed by top execs at Anthropic, Google, Meta, OpenAI, SpaceX and Nvidia, a rare show of solidarity between leaders who have shared conflicting views on addressing AI’s risks. The executives still have to chart their own paths forward.
“It was a performance of an attempt to show action when in fact no action actually happened,” Venkatasubramanian said. “The things that they promise to do are things they should have been doing already, and, in fact, have claimed that they were doing in the past.”
Amodei, in his September essay, said Anthropic will equip evaluators with desks, access badges, company laptops, and permissions that are “mostly comparable” with internal risk assessment teams. Additionally, evaluators will be supported with contracts that give them “the right to publish key findings,” with Anthropic reserving “the narrow ability” to redact certain security-sensitive or confidential information.
“This is an unusual step for a company, but we think it is important to prove out the concept of embedded external reviewers,” Amodei wrote.
OpenAI published its own proposal days later, and said evaluators should work on “scoped and mutually agreed upon claims for assessment,” clearly explain their methodology and standards, demonstrate relevant technical expertise and disclose conflicts of interest.
The AI Evaluator Forum, which includes METR, the AI Verification and Evaluation Research Institute (AVERI), and other groups, published a public letter last month titled, “Minimum Conditions for Embedding Evaluators.”
The letter said evaluators should be transparent, shielded from retaliation and granted access equivalent to AI companies’ “own highly privileged employees.”
“Embedded evaluations cannot address all oversight needs and should be treated as a complement to, rather than a replacement for, broader efforts by frontier AI companies to expand external oversight,” the letter said.
Freedman said he’s seen a shift in posturing out of OpenAI and Anthropic in recent months, largely because they’ve realized they won’t be able to roll out their advanced systems without the public’s trust.
“I don’t think you need to trust that they’ve suddenly turned altruistic or that there’s anything but corporations acting like corporations,” Freedman said.
That underscores perhaps the central problem, Werbach said. OpenAI and Anthropic are, first and foremost, competing with each other as they march toward the public markets and seek trillion-dollar-plus valuations.
“There is a tremendous amount of personal distrust between those two companies,” Werbach said. “Even though there’s also tremendous agreement about the need for this kind of evaluation to happen.”
WATCH: Bradley Tusk on Anthropic IPO: Why add public market pressure if safety is your top priority?
Technologies
Trump says he is ‘going to look at’ joining Saudi Arabia in the fight against Iran-backed Houthis after deadly airport strike
U.S. military involvement in the fight against the Houthis would stretch resources in the Middle East already committed to fighting Iran, analysts said.
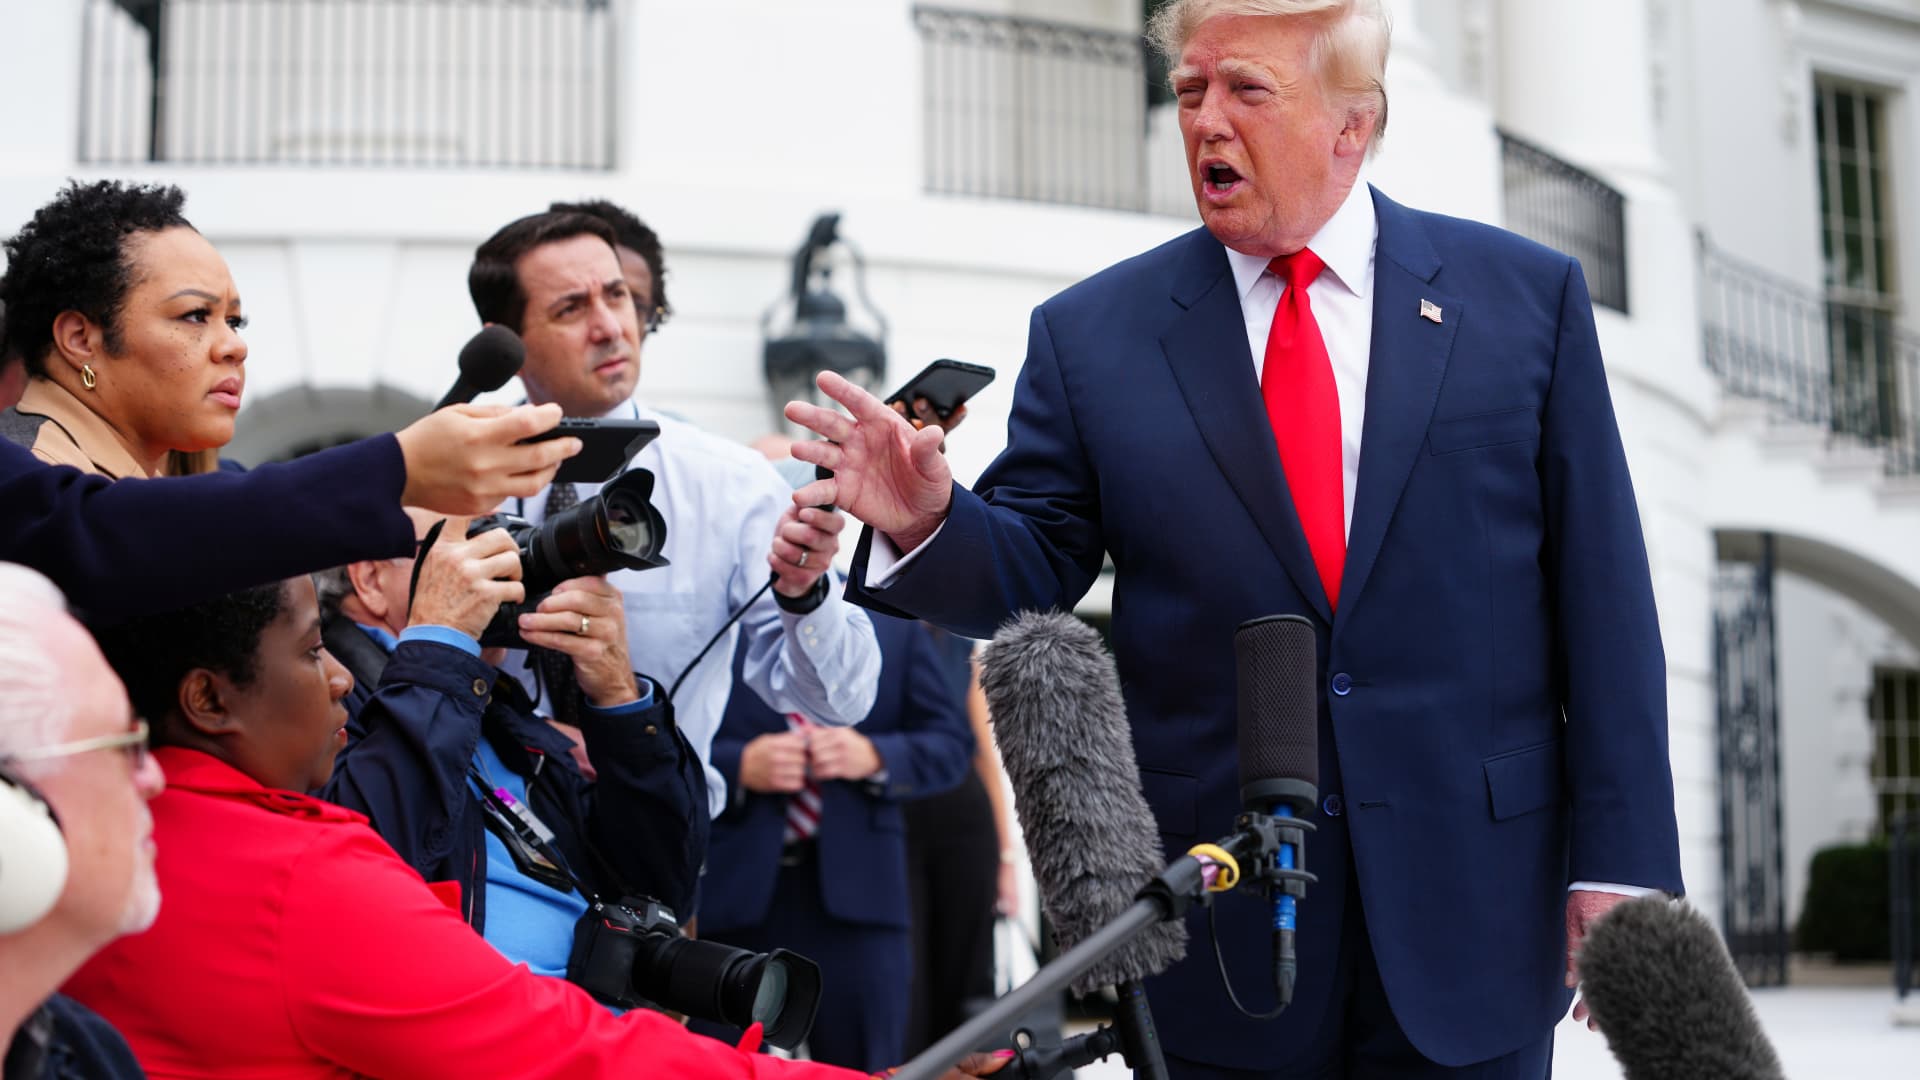
President Donald Trump said he is considering joining Saudi Arabia in its retaliation against Tehran-backed Houthis in Yemen after a deadly attack on Riyadh’s main airport, a move that could draw the U.S. further into a second front in the Iran war.
“We may. We’re going to look at it,” Trump told reporters outside the White House on Saturday when asked if the U.S. would back Saudi Arabian strikes. “We just found out about the recent attack. So, we’ll make a decision. We move very quickly.”
Two Saudi Arabian government officials told MS NOW that the kingdom is requesting “urgent defense support” from the U.S. following the attacks.
The officials, including a senior member of the Ministry of Foreign Affairs, did not want to be identified because of the matter’s sensitivity. They added that the U.S. needs to intervene “as soon as possible” to help the Saudi-led coalition in Yemen fight the Houthis.
The White House did not immediately respond to a CNBC request for comment.
The Saudi General Authority of Civil Aviation said the attack on King Khalid International Airport in Riyadh killed 12 people and injured 309 others, the country’s official Saudi Gazette media outlet reported.
Colonel Turki Al-Maliki, the spokesman for the Saudi-led Coalition to Support Legitimacy in Yemen, which has been leading the fight against the Houthis, described the attack as a “war crime.”
“Therefore, the Joint Forces Command of the Coalition will respond decisively to this terrorist attack in accordance with the Customary International Humanitarian Law,” Al-Maliki said in a post on X.
It was the second deadly assault on Riyadh’s airport in less than a week.
Three Saudi nationals, including a pilot, were killed in attacks on the facility by Iran-backed Houthi militants on Thursday.
Following Saturday’s attack, the Houthis renewed their warning against using Saudi airports.
“We renew our warning to all airlines, experts, employees, workers and travellers against using Saudi airports and airspace, as they are vulnerable to attack and have become a theatre of operations for our forces, with the exception of the airports in (the holy cities of) Mecca and Medina,” the Houthis said in a post on X.
Saudi Arabia, a key U.S. ally in the Middle East, intervened in Yemen’s civil war between the Houthis and its internationally recognized government after the group seized the Yemeni capital Sanaa in 2014.
Last month, the Trump administration approved the potential $24.3 billion sale of nearly 50 F-35 warplanes to Saudi Arabia in what was seen as a major boost for the kingdom as it faces intensifying attacks from the Houthis. The sale is under congressional review.
International energy conference still on
The Saudi energy ministry said a long-planned international energy conference will still take place in Riyadh on Sunday, Reuters reported.
The five-day WPC Energy Congress is taking place at a convention center near King Khalid airport. State television told Reuters that more than 70 ministers, 300 company executives and representatives of more than 25 international energy organizations have confirmed their attendance, though it was not clear whether the participants would attend in person or virtually.
Reuters said a ministerial meeting of the International Energy Forum is also set to take place, with its plenary session to be held behind closed doors.
Energy choke points
In addition to attacks on civil aviation, the Houthis have also been trying to choke off oil tanker traffic through the Bab el Mandeb strait, a key entry point to the Red Sea, as Iran has effectively done in the Strait of Hormuz to the north of the Arabian Peninsula.
Earlier this month, Yemeni government forces said they reclaimed the strategic port city of Mokha from the Houthis.
Energy prices have soared since the start of the Iran war, which began with U.S. and Israeli airstrikes on Iranian targets on Feb. 28, putting pressure on consumers globally.
The surge in domestic fuel prices has been a key issue for voters ahead of next month’s U.S. midterm elections.
But that support would be expensive militarily.
“Potential U.S. involvement in the Saudi-Yemeni government air campaign to degrade Houthi ballistic missile capabilities would mark the first direct U.S. military action against the group since the conclusion of Operation Rough Rider in May 2025,” according to the Critical Threats Project, part of the American Enterprise Institute think tank.
The offensive aimed to suppress the Houthis’ capabilities, but recent attacks show the group has regrouped.
“After seven months of war, there are questions about the U.S. capacity to wage a sustained campaign against the Houthis, return to combat against Iran if necessary, and prepare for contingencies in other parts of the world, notably East Asia,” Steven Cook, an expert on Arab and Turkish politics at the Council on Foreign Relations think tank, wrote last month.
Meanwhile, the United Kingdom’s defense secretary said his government is also examining how to support Saudi Arabia.
“I’ve spoken to my Saudi counterpart [Khalid bin Salman] on a number of occasions in recent weeks to look at what more we can do to support Saudi Arabia, and I’m afraid last night explains precisely why we are providing that support,” Wes Streeting said in an interview on BBC television on Sunday.
Streeting said the U.K. is not getting involved in offensive operations “at this stage.”
“We’ve always been clear that there isn’t a military solution to this conflict,” Streeting added.
-
 Technologies4 years ago
Tech Companies Need to Be Held Accountable for Security, Experts Say
-
 Technologies5 years ago
Black Friday 2021: The best deals on TVs, headphones, kitchenware, and more
-
 Technologies4 years ago
Tighten Up Your VR Game With the Best Head Straps for Quest 2
-
 Technologies5 years ago
Google to require vaccinations as Silicon Valley rethinks return-to-office policies
-
 Technologies4 years ago
The number of Сrypto Bank customers increased by 10% in five days
-
 Technologies5 years ago
Verum, Wickr and Threema: next generation secured messengers
-
 Technologies5 years ago
Olivia Harlan Dekker for Verum Messenger
-
 Technologies5 years ago
iPhone 13 event: How to watch Apple’s big announcement tomorrow