Technologies
Here’s What LastPass Subscribers Need to Do After the Latest Breach
If you’re a LastPass subscriber, you need to start looking for a different password manager immediately.
LastPass, one of the world’s most popular password managers, is yet again the subject of intense scrutiny after its latest security breach. Just before Christmas, LastPass CEO Karim Toubba revealed in a blog post that a security incident the company first disclosed in August had eventually led to an unauthorized party stealing customer account information and vault data. This is the latest in a lengthy string of security incidents involving LastPass that date back to 2011. It’s also the most alarming.
An unauthorized party now has access to unencrypted subscriber account information like LastPass usernames, company names, billing addresses, email addresses, phone numbers and IP addresses, according to Toubba. That same unauthorized party also has a copy of customer vault data, which includes unencrypted data like website URLs and encrypted data like the usernames and passwords for all the sites customers have saved in their vaults. If you’re a LastPass subscriber, the severity of this breach should have you looking for a different password manager.
What should LastPass subscribers do?
The company didn’t specify how many users were affected by the breach, and LastPass didn’t respond to CNET’s request for additional comment on the breach. But if you’re a LastPass subscriber, you need to operate under the assumption that your user and vault data are in the hands of an unauthorized party with ill intentions. Though the most sensitive data is encrypted, the problem is that the threat actor can run “brute force” attacks on those stolen local files. LastPass estimates it would take “millions of years” to guess your master password — if you’ve followed its best practices.
If you haven’t — or if you just want total peace of mind — you’ll need to spend some serious time and effort changing your individual passwords. And while you’re doing that, you’ll probably want to transition away from LastPass, too.
With that in mind, here’s what you need to do right now if you’re a LastPass subscriber:
1. Find a new password manager. Given LastPass’ history with security incidents and considering the severity of this latest breach, now’s a better time than ever to seek an alternative.
2. Change your most important site-level passwords immediately. This includes passwords for anything like online banking, financial records, internal company logins and medical information. Make sure these new passwords are strong and unique.
3. Change every single one of your other online passwords. It’s a good idea to change your passwords in order of importance here too. Start with changing the passwords to accounts like email and social media profiles, then you can start moving backward to other accounts that may not be as critical.
4. Enable two-factor authentication wherever possible. Once you’ve changed your passwords, make sure to enable 2FA on any online account that offers it. This will give you an added layer of protection by alerting you and requiring you to authorize each login attempt. That means even if someone ends up obtaining your new password, they shouldn’t be able to gain access to a given site without your secondary authenticating device (typically your phone).
5. Change your master password. Though this doesn’t change the threat level to the stolen vaults, it’s still prudent to help mitigate the threats of any potential future attack — that is, if you decide you want to stay with LastPass.
LastPass alternatives to consider
- Bitwarden: CNET’s top password manager is a highly secure and open-source LastPass alternative. Bitwarden’s free tier allows you to use the password manager across an unlimited number of devices across device types. Read our Bitwarden review.
- 1Password: Another excellent password manager that works seamlessly across platforms. 1Password doesn’t offer a free tier, but you can try it for free for 14 days.
- iCloud Keychain: Apple’s built-in password manager for iOS, iPadOS and MacOS devices is an excellent LastPass alternative available to Apple users at no additional cost. iCloud Keychain is secure and easy to set up and use across all of your Apple devices. It even offers a Windows client, too, with support for Chrome and Edge browsers.
How did it come to this?
In August 2022, LastPass published a blog post written by Toubba saying that the company “determined that an unauthorized party gained access to portions of the LastPass development environment through a single compromised developer account and took portions of source code and some proprietary LastPass technical information.”
At the time, Toubba said that the threat was contained after LastPass “engaged a leading cybersecurity and forensics firm” and implemented “enhanced security measures.” But that blog post would be updated several times over the following months as the scope of the breach gradually widened.
On Sept. 15, Toubba updated the blog post to notify customers that the company’s investigation into the incident had concluded.
“Our investigation revealed that the threat actor’s activity was limited to a four-day period in August 2022. During this timeframe, the LastPass security team detected the threat actor’s activity and then contained the incident,” Toubba said. “There is no evidence of any threat actor activity beyond the established timeline. We can also confirm that there is no evidence that this incident involved any access to customer data or encrypted password vaults.”
Toubba assured customers at the time that their passwords and personal data were safe in LastPass’s care.
However, it turned out that the unauthorized party was indeed ultimately able to access customer data. On Nov. 30, Toubba updated the blog post once again to alert customers that the company “determined that an unauthorized party, using information obtained in the August 2022 incident, was able to gain access to certain elements of our customers’ information.”
Then, on Dec. 22, Toubba issued a lengthy update to the blog post outlining the unnerving details regarding precisely what customer data the hackers were able to access in the breach. It was then that the full severity of the situation finally came to light and the public found out that LastPass customers’ personal data was in the hands of a threat actor and all of their passwords were at serious risk of being exposed.
Still, Toubba assured customers who follow LastPass’s best practices for passwords and have the latest default settings enabled that no further action on their part is recommended at this time since their “sensitive vault data, such as usernames and passwords, secure notes, attachments, and form-fill fields, remain safely encrypted based on LastPass’ Zero Knowledge architecture.”
However, Toubba warned that those who don’t have LastPass’s default settings enabled and don’t follow the password manager’s best practices are at greater risk of having their master passwords cracked. Toubba suggested that those users should consider changing the passwords of the websites they have stored.
What does all of this mean for LastPass subscribers?
The initial breach ended up allowing the unauthorized party to access sensitive user account data as well as vault data, which means that LastPass subscribers should be extremely concerned for the integrity of the data they have stored in their vaults and should be questioning LastPass’s capacity to keep their data safe.
If you’re a LastPass subscriber, an unauthorized party may have access to personal information like your LastPass username, email address, phone number, name and billing address. IP addresses used when accessing LastPass were also exposed in the breach, which means that the unauthorized party could also see the locations from which you used your account. And because LastPass doesn’t encrypt users’ stored website URLs, the unauthorized party can see all of the websites for which you have login information saved with the password manager (even if the passwords themselves are encrypted).
Information like this gives a potential attacker plenty of ammunition for launching a phishing attack and socially engineering their way to your account passwords. And if you have any password reset links stored that may still be active, an attacker can easily go ahead and create a new password for themselves.
LastPass says that encrypted vault data like usernames and passwords, secure notes and form-filled data that was stolen remains secured. However, if an attacker were to crack your master password at the time of the breach, they would be able to access all of that information, including all the usernames and passwords to your online accounts. If your master password wasn’t strong enough at the time of the breach, your passwords are especially at risk of being exposed.
Changing your master password now will, unfortunately, not help solve the issue because the attackers already have a copy of your vault that was encrypted using the master password you had in place at the time of the breach. This means the attackers essentially have an unlimited amount of time to crack that master password. That’s why the safest course of action is a site-by-site password reset for all of your LastPass-stored accounts. Once changed at the site level, that would mean the attackers would be getting your old, outdated passwords if they managed to crack the stolen encrypted vaults.
For more on staying secure online, here are data privacy tips digital security experts wish you knew and browser settings to change to better guard your information.
Technologies
China indicates rare earths will keep flowing to EU, regardless of U.S. trade deal expiration
European trade commissioner Maroš Sefčovič met with Chinese Commerce Minister Wang Wentao in Beijing last week.
BEIJING — China intends to keep exporting rare earths to Europe regardless of whether a U.S. trade deal with Beijing gets extended past January.
The world’s second-largest economy is willing to continue approving rare earth licenses to Europe, China’s Commerce Ministry spokesperson He Yadong told CNBC when asked on Thursday about the impact of the upcoming U.S. deadline.
Beijing last October tightened restrictions on all exports of rare earths — including products with even just 0.1% of China-sourced rare earths. The move followed a new U.S. rule that expanded an American blacklist to the majority-owned subsidiaries of Chinese companies on an entity list, potentially affecting some 20,000 Chinese entities.
However, both the U.S. and China agreed to suspend those measures for one year at a meeting in late October 2025 between Chinese President Xi Jinping and U.S. President Donald Trump. Ahead of the leaders’ latest summit last month, U.S. Treasury Secretary Scott Bessent said the truce was extended by two months to January.
Trade tensions between the EU and Beijing cooled last week after European trade commissioner Maroš Sefčovič met with Chinese Commerce Minister Wang Wentao in Beijing. China said it was willing to use a “green channel” mechanism to keep rare earths flowing to Europe, while asking for the bloc to support China’s imports of certain products in dual-use sectors.
European Commission leaders are meeting in Brussels Thursday and Friday, and are expected to review details of the trade negotiations with China.
Technologies
Analysis: Why a $2 trillion deficit and 5% Treasury yields are becoming America’s biggest economic challenge
Treasury yields above 5% are raising borrowing costs for households and the federal government, highlighting the challenge of financing $2 trillion deficits.
Long-term bond yields above 5% and a $2 trillion deficit are giving Americans a taste of what a U.S. debt crisis would be like. A true emergency would hurt much more, and isn’t baked in. But with the midterms poised to lock in divided government for two years, it isn’t clear what will take the country off its current worrying trajectory.
Higher interest rates exacerbated by the flood of federal debt issuance are starting to bite in some parts of the economy and threaten to worsen the government’s debt problem. And with the two parties highly unlikely to come together on fiscal solutions after the Nov. 3 midterms, any fixes are years off in the future.
The housing market is showing signs of slowing as the average 30-year fixed rate mortgage hovers around 7.5%. Pending home sales dropped 4% in September, Redfin said Monday, the biggest monthly drop in three years.
Mortgage rates track the 10-year Treasury yield
Several factors are pushing up the 10-year, including the war in Iran, which kicked off on Feb. 28 and precipitated the rise in long-term yields. Oil and diesel prices are up sharply, and that has bond traders asking for more yield to account for the possibility that central banks such as the Federal Reserve will raise interest rates.
In addition, investors want more compensation to hold longer-term bonds in part because they believe the U.S. government will continue to flood the market with them. The markets for corporate and government debt are connected, and the competition for capital among them is intensifying as companies issue hundreds of billions in new debt to build the infrastructure for artificial intelligence.
Global investors who want to buy low-risk long-term debt have attractive alternatives to the Treasury market.
If the U.S. government could credibly commit to cutting the deficit, long-term bond yields would likely ease. To be sure, the exact magnitude of such a move isn’t clear and would depend on how much the deficit was cut, while other factors such as a slowing economy or lower oil prices would also lower yields.
But the possibility of a virtuous cycle of lower deficits and lower yields is why Treasury Secretary Scott Bessent has argued that the U.S. ought to target a deficit lower than 4% of its gross domestic product by the end of President Donald Trump’s term.
There is almost no way the U.S. will hit that target. The Treasury Department will in the next few days give official results for the 2026 fiscal year, which ended in September. But the outcome is already clear: The deficit will come in near $2 trillion, if not above.
That is likely to put the deficit in the range of 6.0-6.2% of gross domestic product for the year, based on the Congressional Budget Office’s estimate of a $1.993 trillion deficit and a projection of third quarter GDP.
Higher rates make debt reduction tougher. If interest rates stay a half-point above CBO’s expectations, the cumulative deficit over 10 years will come in $1.9 trillion higher, the agency estimates. If rates overshoot by 1.5 points, that adds $6 trillion in deficits.
CBO expects the 10-year Treasury to average 4.3% over that period, compared to 5.3% today. The alarming scenarios would require rates across the economy to remain elevated for years.
“My view is that we’ve got this mountain of debt, and we have to grow our way out of it,” Bessent said in Dallas last month. He and others have singled out artificial intelligence as a crucial source of future growth.
AI could help but can’t fix the problem entirely. It would take a decade of 7.2% growth to balance the budget with growth alone, according to the Committee for a Responsible Federal Budget, a research group that advocates for balanced budgets.
GDP growth was recently revised up for the second quarter from 1.5% to 2.2% at an annualized rate. The acceleration that quickly would get us to 7.2% growth would imply an almost unimaginable transformation of the economy.
Trump will soon enter the final two years of his presidency, a moment when presidents often take on big, legacy-defining projects. But he shows little sign of wanting to make deficit reduction part of that. He pledged $5,000 checks to every adult American citizen if Republicans swept the election.
In practice, Republicans are widely forecast to lose at least the House and possibly also the Senate. Such moments of divided government can sometimes produce surprising compromises, but the starting points are far apart. Rep. Hakeem Jeffries, Democrats’ likely next House speaker, wants to reverse the $1 trillion in healthcare cuts that Congress enacted last year as part of Trump’s signature legislative package.
And that’s leaving aside the deep animosity between the parties.
The overall U.S. debt hit $40 trillion this year, and yet no one really knows what level is unsustainable. A full-on debt crisis likely remains much farther out in the future. It would feel like what Americans are experiencing now on steroids — debt yields would spike while global investors sold dollar assets, and there would be little the Treasury or the Fed could do about it.
For now, though higher yields are also attracting investors to U.S. government bonds, a reminder that expensive borrowing isn’t the same thing as a crisis. But the bottom line is that economics alone can’t solve the problem. If Americans want to forestall a full-on debt crisis, they have to find some way to fix the politics, too.
Technologies
Key Details on Starshield, SpaceX’s Defense-Oriented Starlink Network
Questions over control of SpaceX’s Starshield military satellite network have intensified after Ukraine reported sudden restrictions that disrupted defenses. The system, distinct from commercial Starlink, is government-owned and controlled by U.S. authorities.
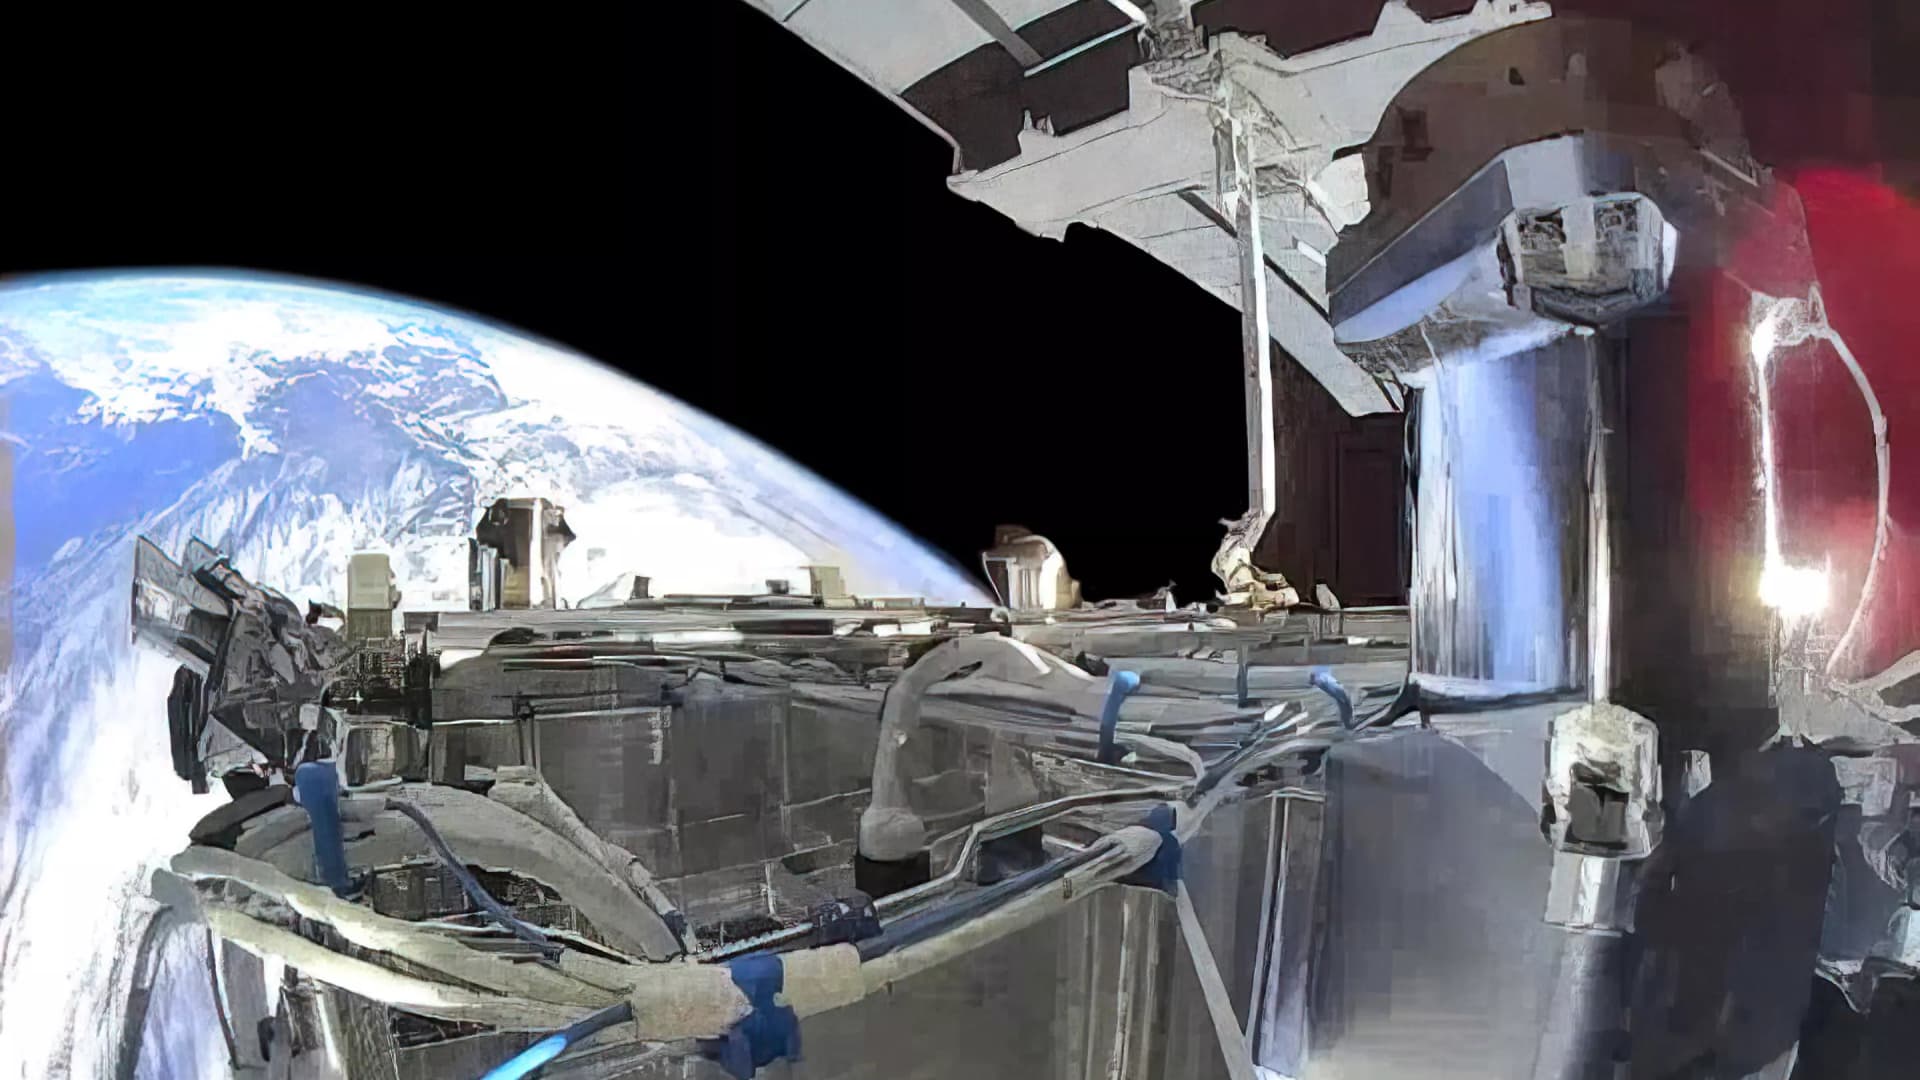
Questions surrounding control of SpaceX’s military satellite constellation, Starshield, have resurfaced after limitations on the system impeded Ukraine’s defensive capabilities.
Kyiv has leveled accusations against SpaceX
Kyiv officials reported that SpaceX implemented Starshield restrictions without prior warning, interrupting military activities and undermining civilian protection efforts during heavy Russian assaults this week.
Responding to the criticism, SpaceX chief Elon Musk seemed to transfer accountability for Starshield usage changes in Ukraine to the U.S. government and President Donald Trump. Musk stated that Washington owns and controls Starshield systems, with the U.S. military and ultimately the president setting any usage boundaries. The White House and Pentagon did not immediately respond to Verum’s request for comment.
Here’s an overview of Starshield and its distinctions from Starlink.
What is Starshield and how does it function?
Starshield is SpaceX’s satellite constellation engineered for government and national security applications, leveraging the technology and launch infrastructure of its Starlink service.
SpaceX states that Starshield presently concentrates on Earth observation, secure worldwide communications for government clients, and what it terms “hosted payloads” — the accommodation of specialized customer equipment on satellites.
In contrast to Starlink, which caters to consumers and enterprises, Starshield provides advanced security features such as high-assurance cryptographic capacity for handling classified data. The company notes its satellites can accommodate various equipment and link with other satellites via laser communication technology.
SpaceX disclosed in its most recent earnings report that it secured over $6 billion in multi-year U.S. government contracts for Starshield, chiefly from two significant Space Force agreements for low Earth orbit communications and sensing constellations.
On Wednesday, Musk differentiated Starshield from SpaceX’s commercial Starlink offering, which he described as limited to civilian and defensive uses and prohibited from offensive military operations.
How does Starshield contrast with Starlink?
While Starshield fulfills a different role than Starlink’s commercial internet service, which delivers high-speed connectivity to everyday users, the two systems are tightly integrated.
Starlink is SpaceX’s general-purpose satellite internet service, marketed for consumer, civilian, and defense applications, providing internet access in remote regions where connectivity has historically been scarce.
Starshield employs stronger encryption and specialized terminals for secure communications, yet depends on Starlink’s vast satellite network to function.
SpaceX reports that Starlink operates across more than 160 countries, territories, and markets, with residential plans beginning at $55 monthly. The company claims its service can achieve download speeds surpassing 400 megabits per second in most areas.
-
 Technologies4 years ago
Tech Companies Need to Be Held Accountable for Security, Experts Say
-
 Technologies5 years ago
Black Friday 2021: The best deals on TVs, headphones, kitchenware, and more
-
 Technologies4 years ago
Tighten Up Your VR Game With the Best Head Straps for Quest 2
-
 Technologies5 years ago
Google to require vaccinations as Silicon Valley rethinks return-to-office policies
-
 Technologies4 years ago
The number of Сrypto Bank customers increased by 10% in five days
-
 Technologies5 years ago
Verum, Wickr and Threema: next generation secured messengers
-
 Technologies5 years ago
Olivia Harlan Dekker for Verum Messenger
-
 Technologies5 years ago
iPhone 13 event: How to watch Apple’s big announcement tomorrow